OT Security Hub
OT security as a board-level risk
Executive intelligence on industrial cyber, OT resilience, supply chain risk, and the frameworks shaping board-level OT decisions for 2026.
6
Executive briefs
5
Events tracked
5
OT signals this week
Latest OT Security Pulse · Nov 11–17, 2026
OT Security Pulse · Nov 17, 2026
Dragos counted 1,266 industrial ransomware incidents in Q3 2026, up 11% on Q2, and saw none that directly manipulated a control system; disruption came through IT, remote access and suppliers.
- 1Dragos Q3: industrial ransomware keeps halting plants without touching control systems
- 2FBI warns AI pentest framework ARTEX is automating intrusions into energy and manufacturers
- 3CISA republishes Siemens advisories for building automation, energy and edge products
Executive Pulse
What matters this week
Week of November 16, 2026
Unauthenticated Remote Code Execution in NGINX: CVE-2026-123633 and CVE-2026-123007
Boards increasingly need visibility into whether OT disruption could affect safety, production, logistics or revenue.
Read context
Board signalRussia's Cold Relic APT Turns One Cloud Breach Into Another
Boards increasingly need visibility into whether OT disruption could affect safety, production, logistics or revenue.
Read context
FrameworkJava4Shell, NGINX2Shell and more: Why we are not at "Yellow", (Wed, Nov 18th)
Boards increasingly need visibility into whether OT disruption could affect safety, production, logistics or revenue.
Read context
Intelligence Map
The OT security landscape
A living map of the domains, frameworks and runtime layers shaping AI security as an operating discipline. Curated by CISO2CISO editorial — click to explore vendors, capabilities and the architecture view.
Featured Insights
Executive briefs to read first
OT Security
Before the Integrator Touches the Plant: What Your Contract Must Require
CISA and the FBI now tell operators to write cybersecurity requirements into integrator contracts and to watch remote access. Procurement and legal need a concrete checklist: named access, recorded sessions, credential ownership and exit obligations, mapped to IEC 62443-2-4.
Read insight →
OT Security
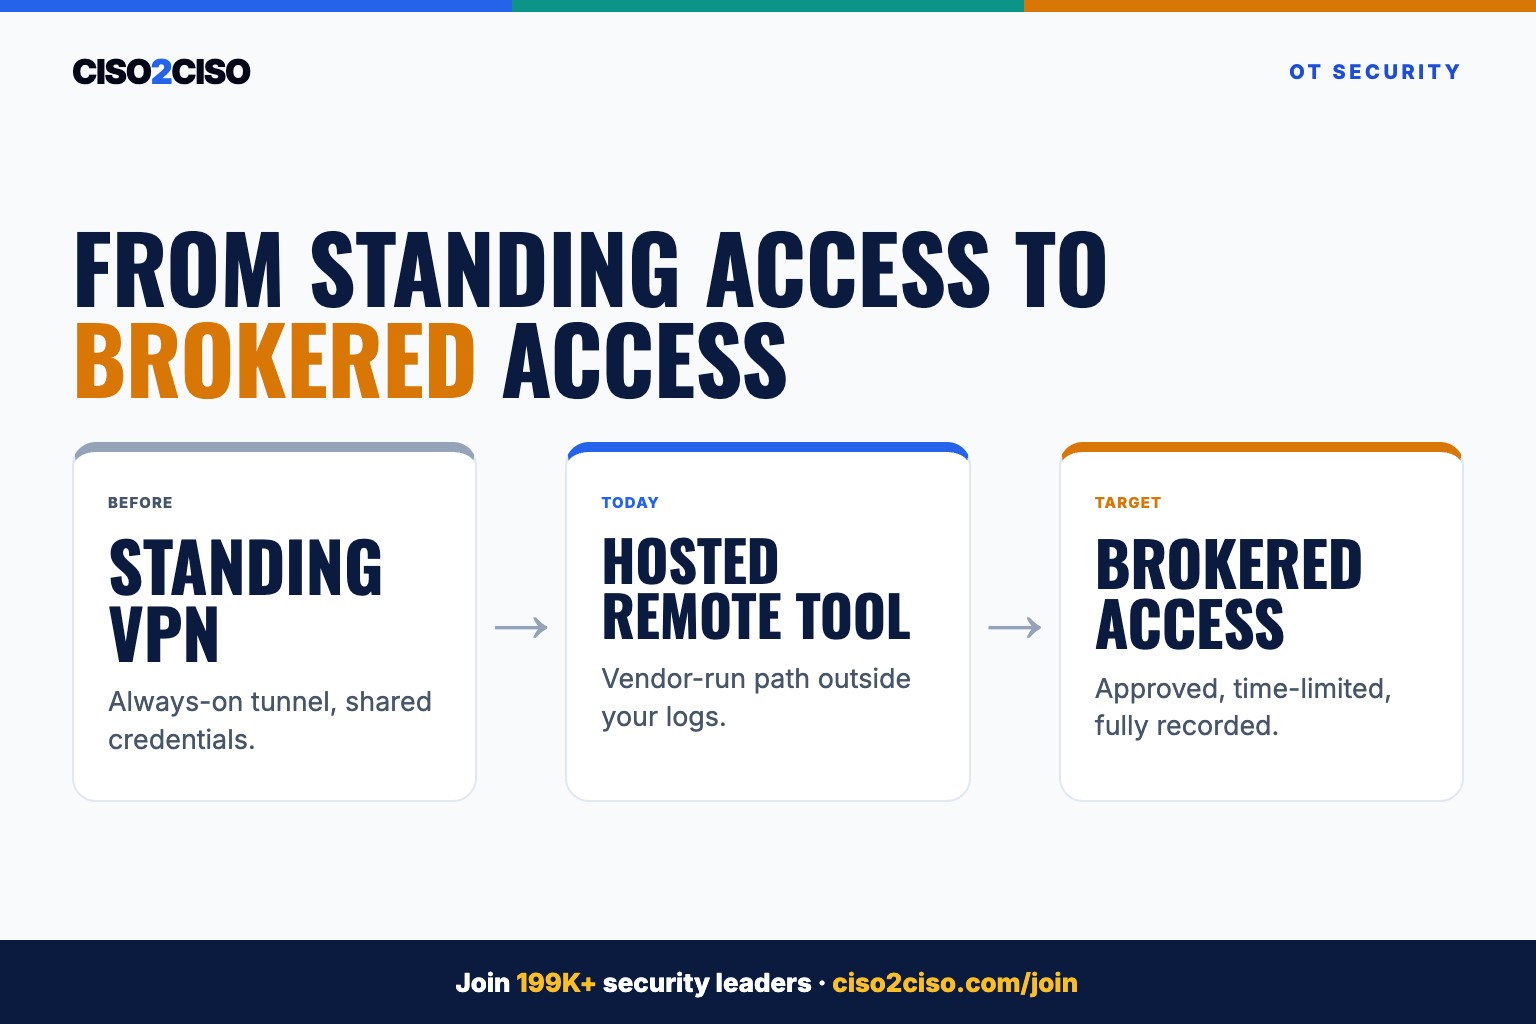
Your Vendor's VPN Is a Standing Invitation Into the Plant
Joint OT guidance co-sealed by the FBI and CISA points to brokered, time-limited, logged vendor access. This note gives CISOs a decision framework to replace standing VPNs and hosted remote-access paths, and the contract terms that make it stick.
Read insight →
OT Security
OT Security Is Becoming a Board-Level Issue
Operational technology risk has crossed the threshold from an engineering concern to a board-level business risk. The organizations that have not made that transition in their governance model are carrying exposure that their boards do not fully understand.
Read insight →
The Latest
Recent executive briefs
OT Security
The Network That Runs the Plant Was Never Built to Be Defended
Operational technology was engineered for availability and safety over decades — long before anyone imagined it would be connected, targeted and held to ransom. Securing it is not a matter of porting IT security into the plant. It requires a different model that respects what the environment was actually built to do.
Read insight →
OT Security
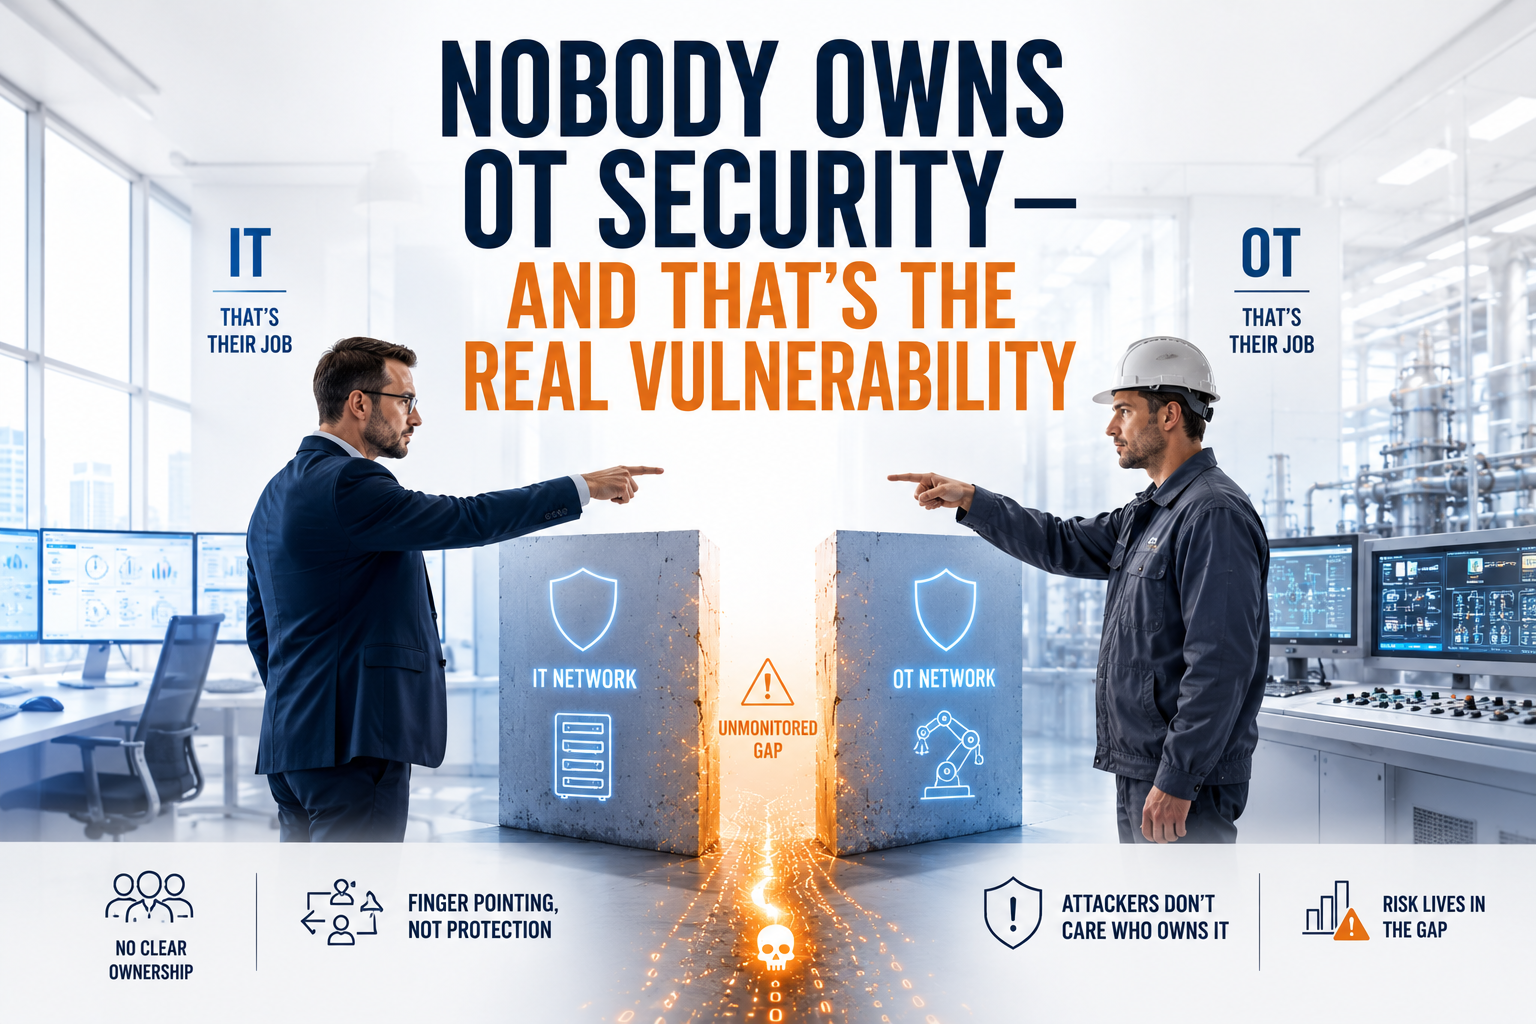
Nobody Owns OT Security — and That's the Real Vulnerability
The most dangerous gap in most industrial environments is not technical. It is organizational: operational technology security falls between the security team, the operations team and the engineers who run the plant, owned fully by none of them. Until accountability is resolved, no amount of tooling will close the gap.
Read insight →
OT Security
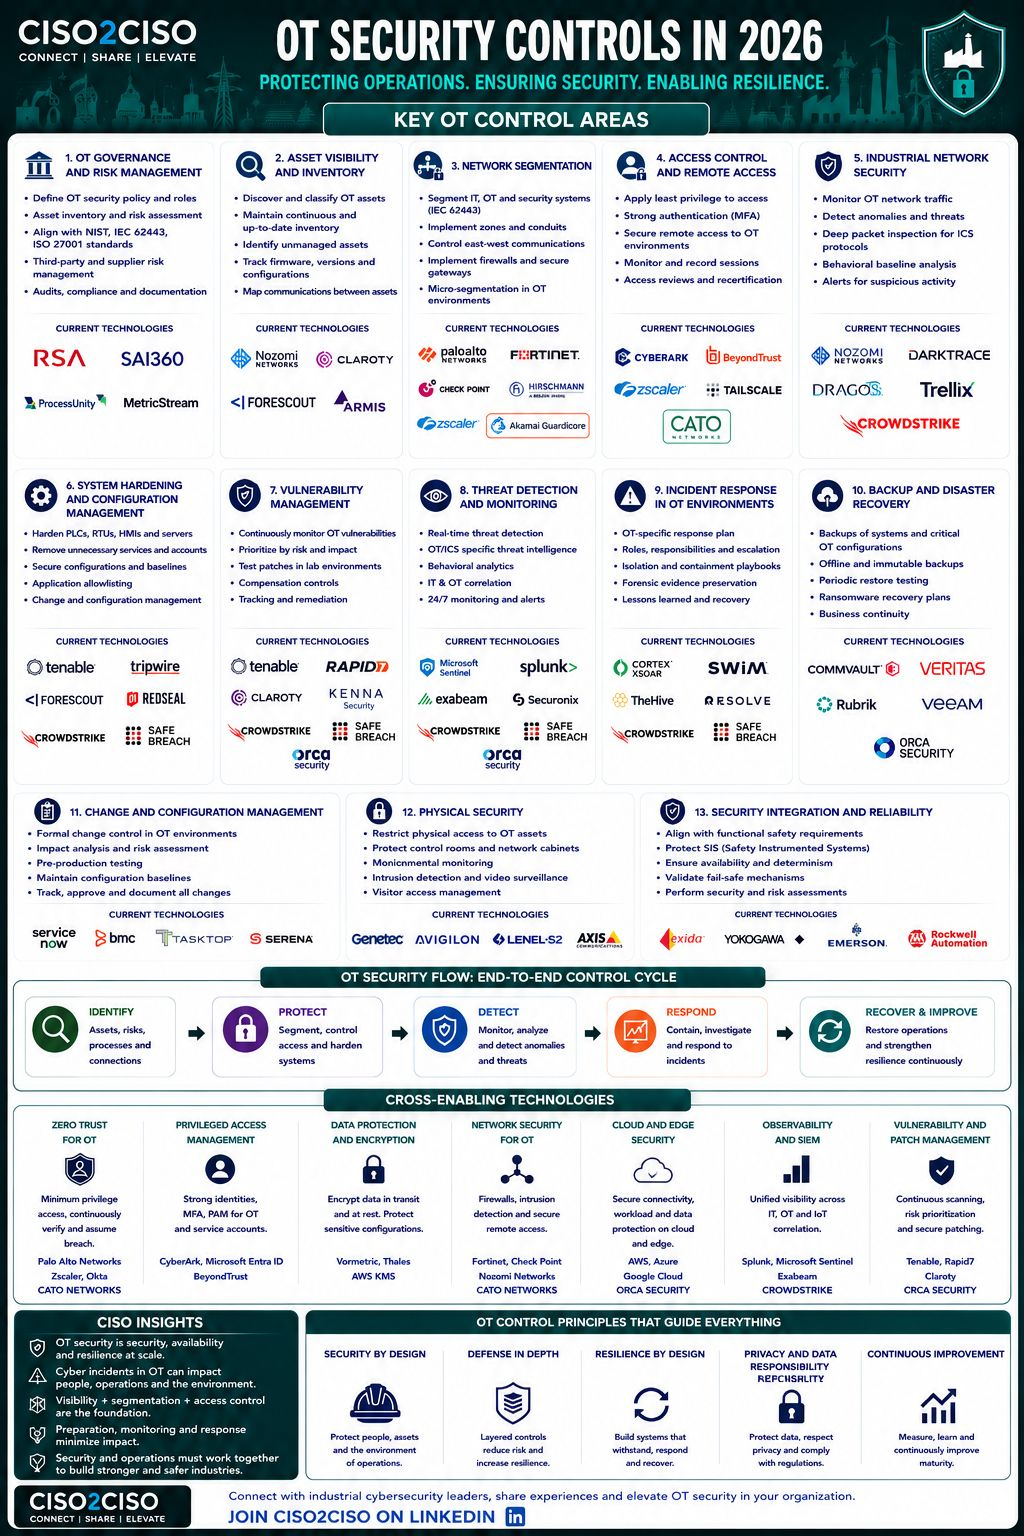
OT Security Is Becoming an Enterprise Resilience Challenge
IT/OT convergence is transforming industrial security from a plant-level protection problem into a strategic business continuity issue. OT incidents now carry consequences that reach far beyond the plant floor — into production, safety, supply chain and regulatory liability.
Read insight →
Industry Signals
Curated intelligence from across the field
Live OT security coverage from trusted sources. Editor's Picks at the top, ranked by source quality, recency and executive relevance.
Boards are demanding cyber metrics tied to resilience and business exposure.
Why it matters — Boards increasingly need visibility into whether OT disruption could affect safety, production, logistics or revenue.
Read story
Industrial cyber resilience is becoming a board-level continuity discussion.
Why it matters — Boards increasingly need visibility into whether OT disruption could affect safety, production, logistics or revenue.
Read story
Engage
Three ways to participate in the OT Security Hub
Subscribe
OT Intelligence Brief
Weekly executive briefing on OT security signals, frameworks and board-level developments.
SubscribeJoin
OT Hub discussion
Closed-door, CISO-only conversation on the OT security operating model.
Request to joinContribute
Submit insight
Share an executive-grade brief, framework, or signal with the Hub. We curate what we publish.
Submit