Author
Marcos Jaimovich
Founder, CISO2CISO
25+ years in cybersecurity, former regional CISO. Founder of CISO2CISO and CISORA.
13 analyses
By Marcos Jaimovich
AI Security
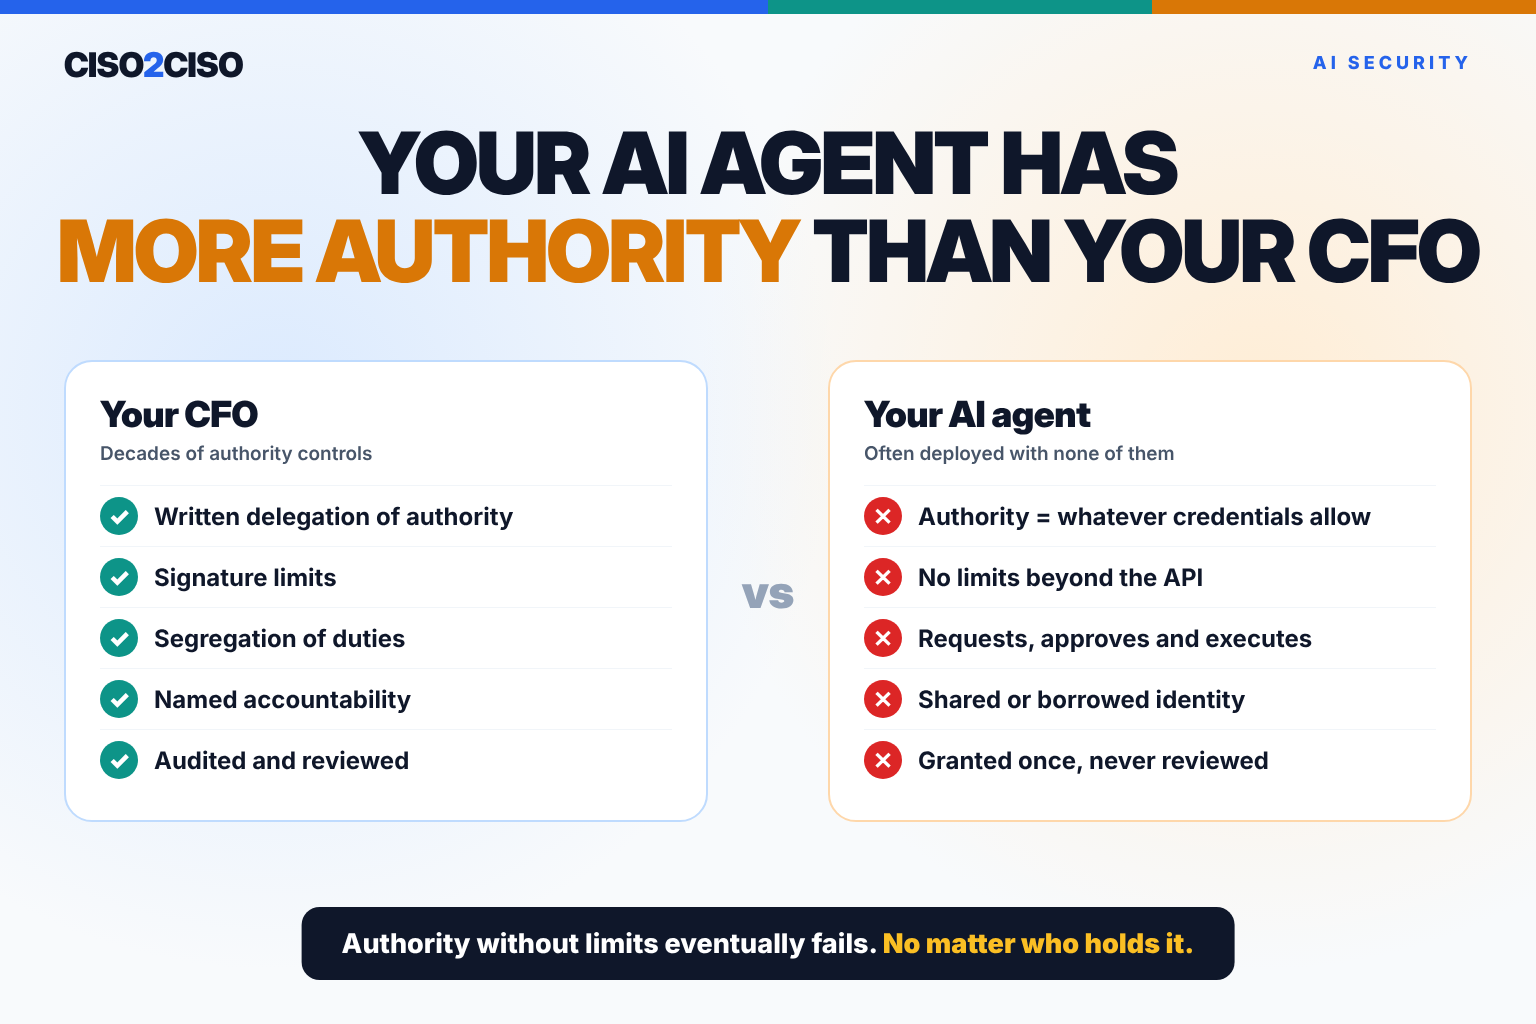
Your AI Agent Has More Authority Than Your CFO
Your CFO cannot move money without signature limits, dual approval and an audit trail. The AI agent your team deployed last quarter may be able to change records, move data and trigger payments with none of those controls. Organizations spent decades building authority controls around their most powerful people — and are now handing comparable authority to software that has no owner, no limits and no reviewer.
Read insight →
Identity Security
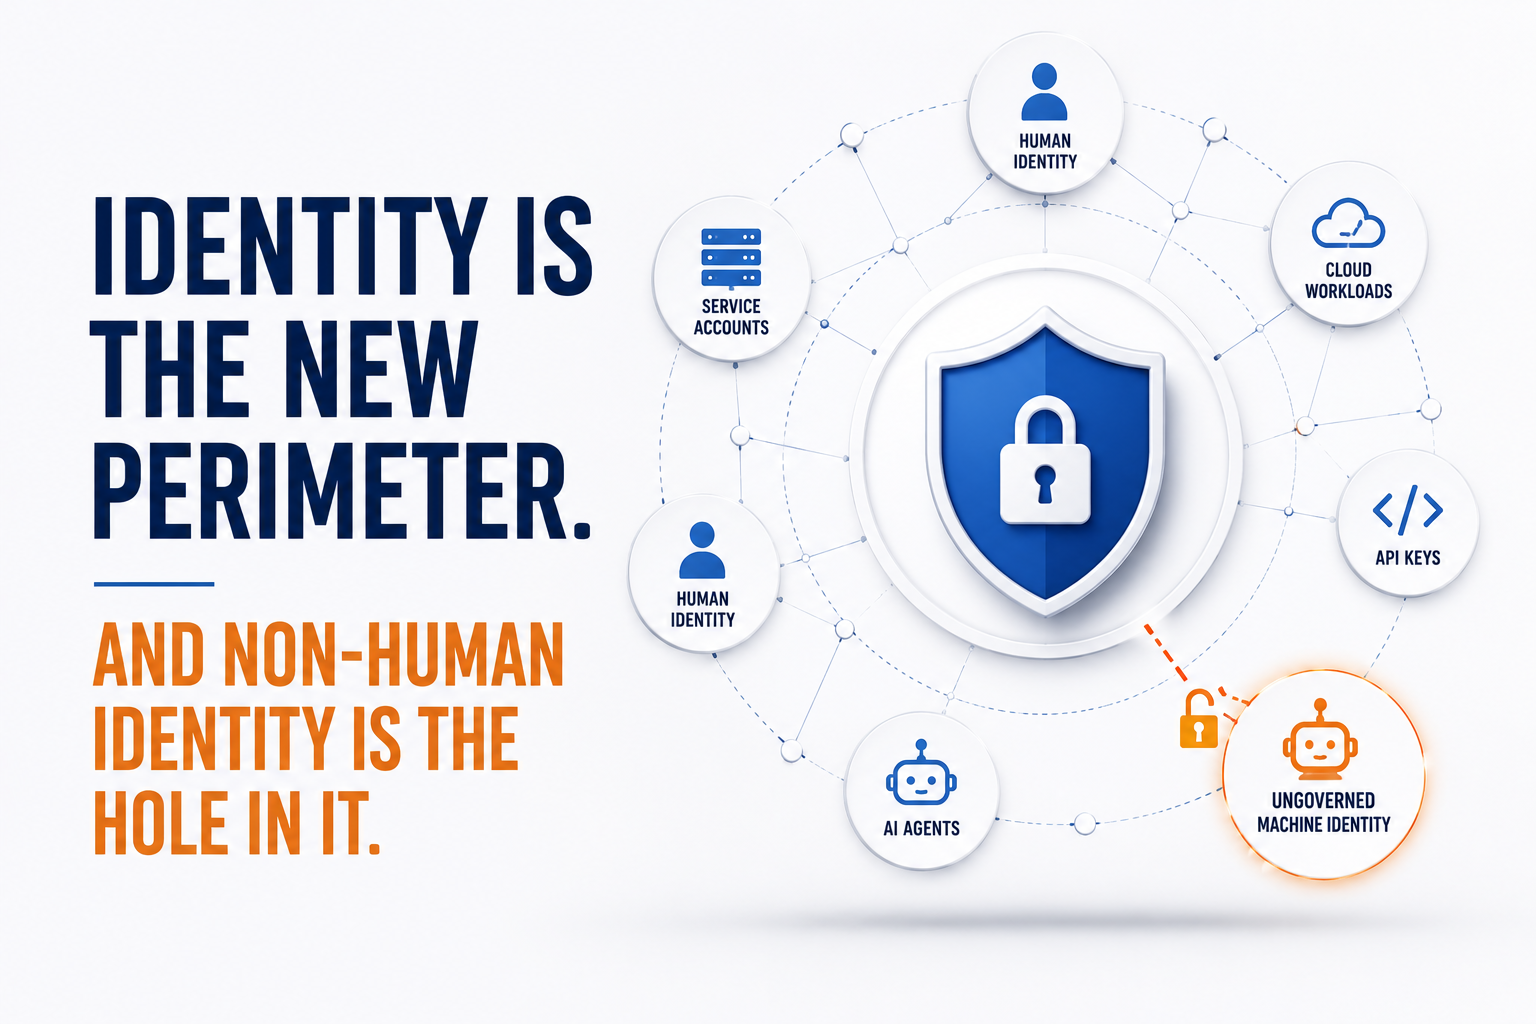
Identity Is the New Perimeter — and Non-Human Identity Is the Hole in It
Most organizations have spent a decade maturing how they govern human identity. In the same period, non-human identities — service accounts, API keys, workload and agent credentials — quietly became the majority of all identities, and almost none of that governance was extended to them. That gap is now one of the highest-priority risks in the enterprise.
Read insight →
Events
The Cybersecurity Events Worth the Flight: A Curated Global Guide to 2026–2027
A deep, curated, region-by-region guide to the cybersecurity events that actually move the industry — from board-level summits to hardcore technical gatherings — across the rest of 2026 and all of 2027. It covers the global flagships and the local scenes that matter, with special depth on Spain, the UK, Brazil, Argentina and the wider Latin American community. Each event includes dates, location, a sharp brief, the recommended audience, and whether it is built for executives, practitioners, or both.
Read insight →
Board Strategy
The Hardest Question a CISO Faces: Could This Happen to Us?
A major ransomware incident hits the news. Ten minutes later the message arrives — the Board wants to see you. Someone asks the question every CISO dreads. This is not a technical question. It is an existential one. And the way you answer it says far more than you think.
Read insight →
Security Operations
How CISOs Should Restructure Security Operations
The security operations model that served enterprises for the past two decades is structurally inadequate for the threat environment of 2026. Restructuring is not a technology problem — it is an organizational and design problem that requires explicit executive choices.
Read insight →
Board Strategy
The Future Cyber Workforce Problem Nobody Is Solving
The cybersecurity industry is focused on how AI will reduce the demand for repetitive security work. Almost nobody is focused on the downstream consequence — that removing the repetitive work also removes the learning environment through which most security expertise has historically been developed.
Read insight →
AI Security
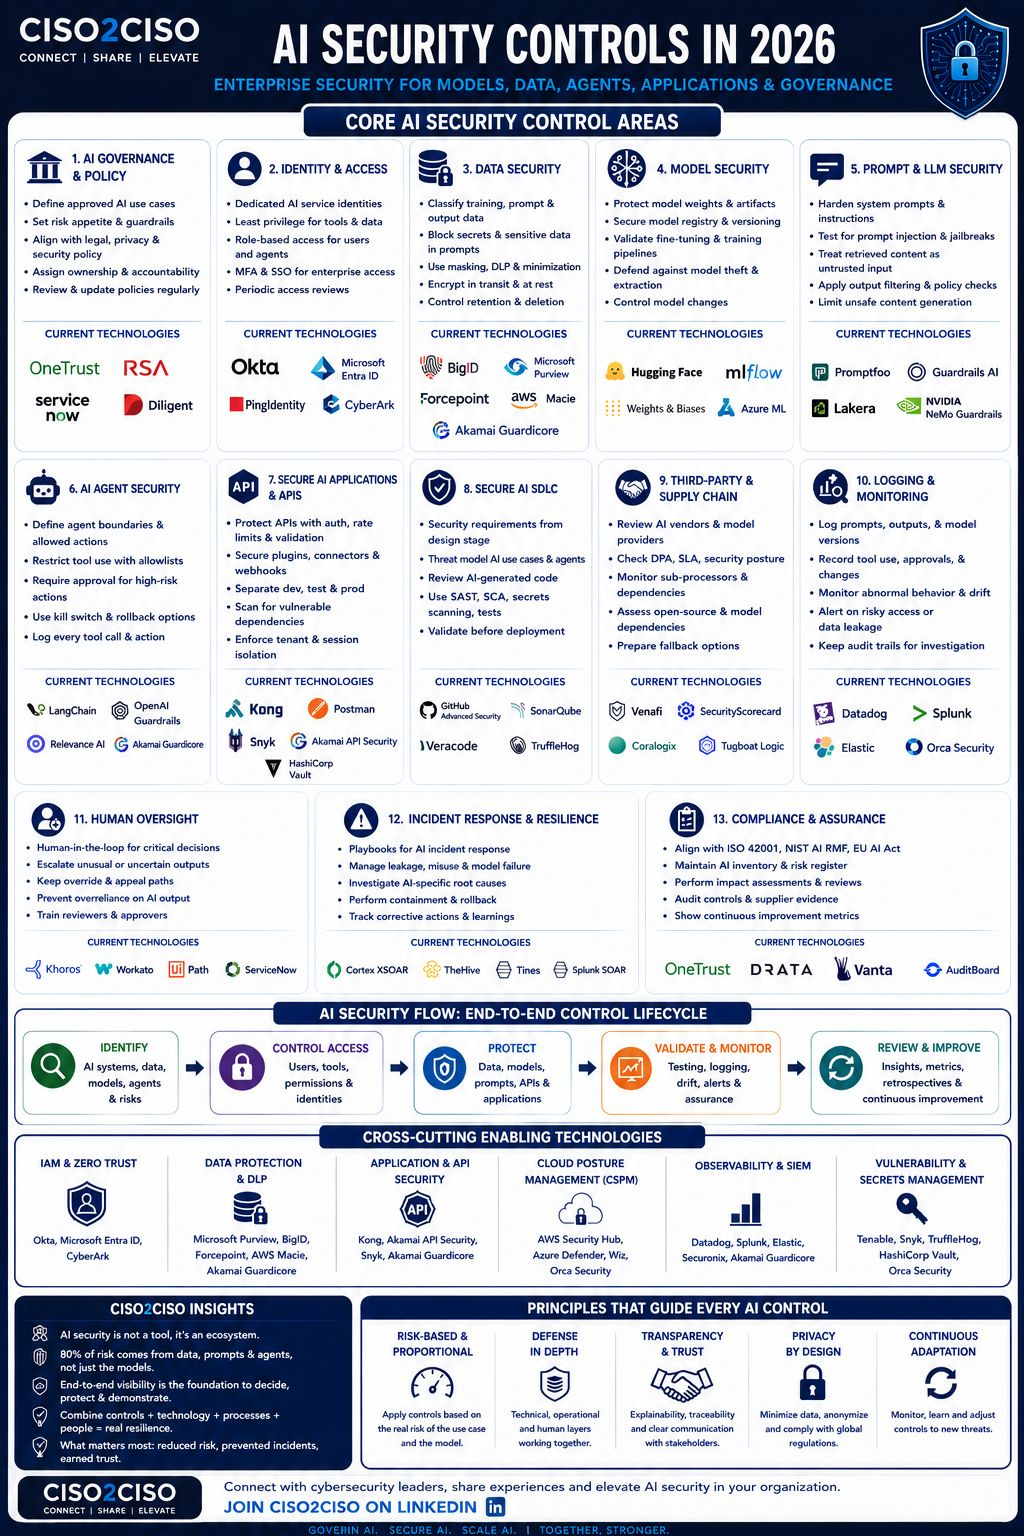
AI Security Is Moving from Frameworks to Operating Models
CISOs are shifting AI security from theoretical controls into implementable ecosystems across models, data, agents, applications and governance. The question is no longer whether controls exist — it is whether they are operational, owned and evidenced.
Read insight →
AI Security
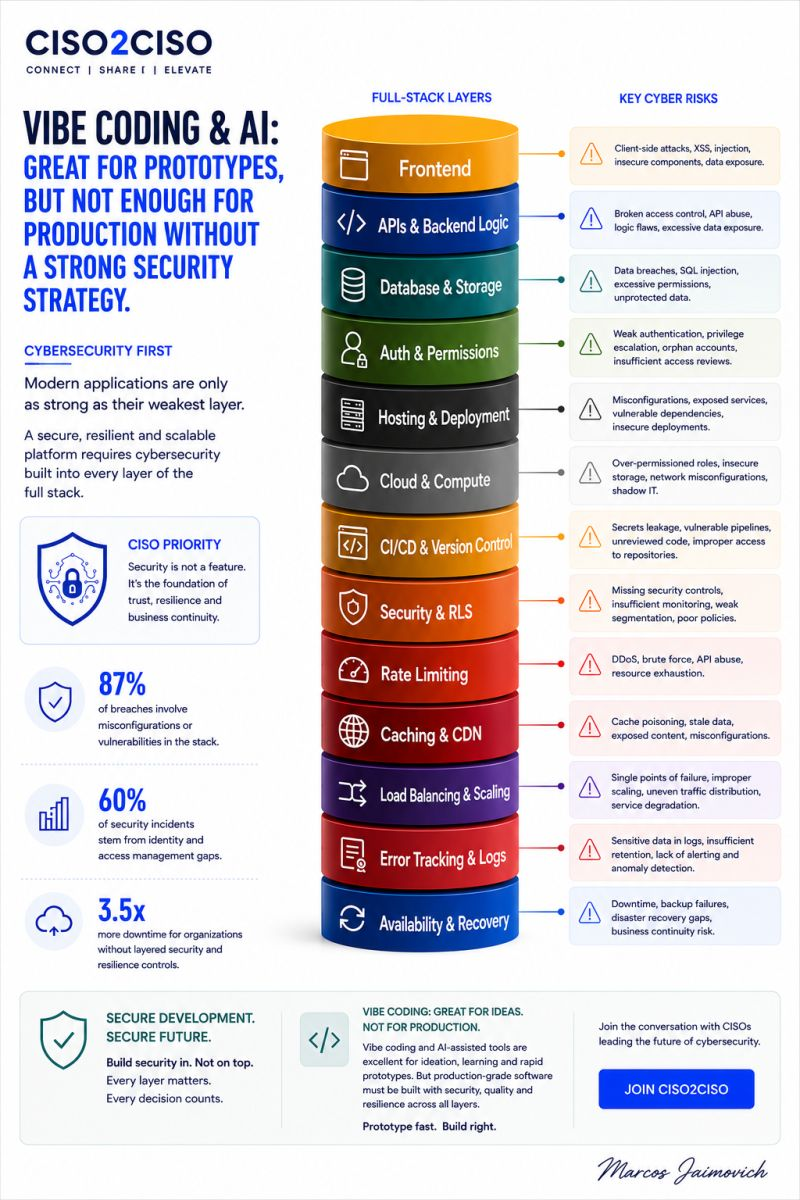
Vibe Coding Accelerates Prototypes — But Production Requires Security Architecture
AI-assisted development is accelerating delivery across enterprise teams. The risk is not the technology — it is the false production maturity that occurs when prototypes move into enterprise environments without the security architecture that production requires.
Read insight →
Threat Intel
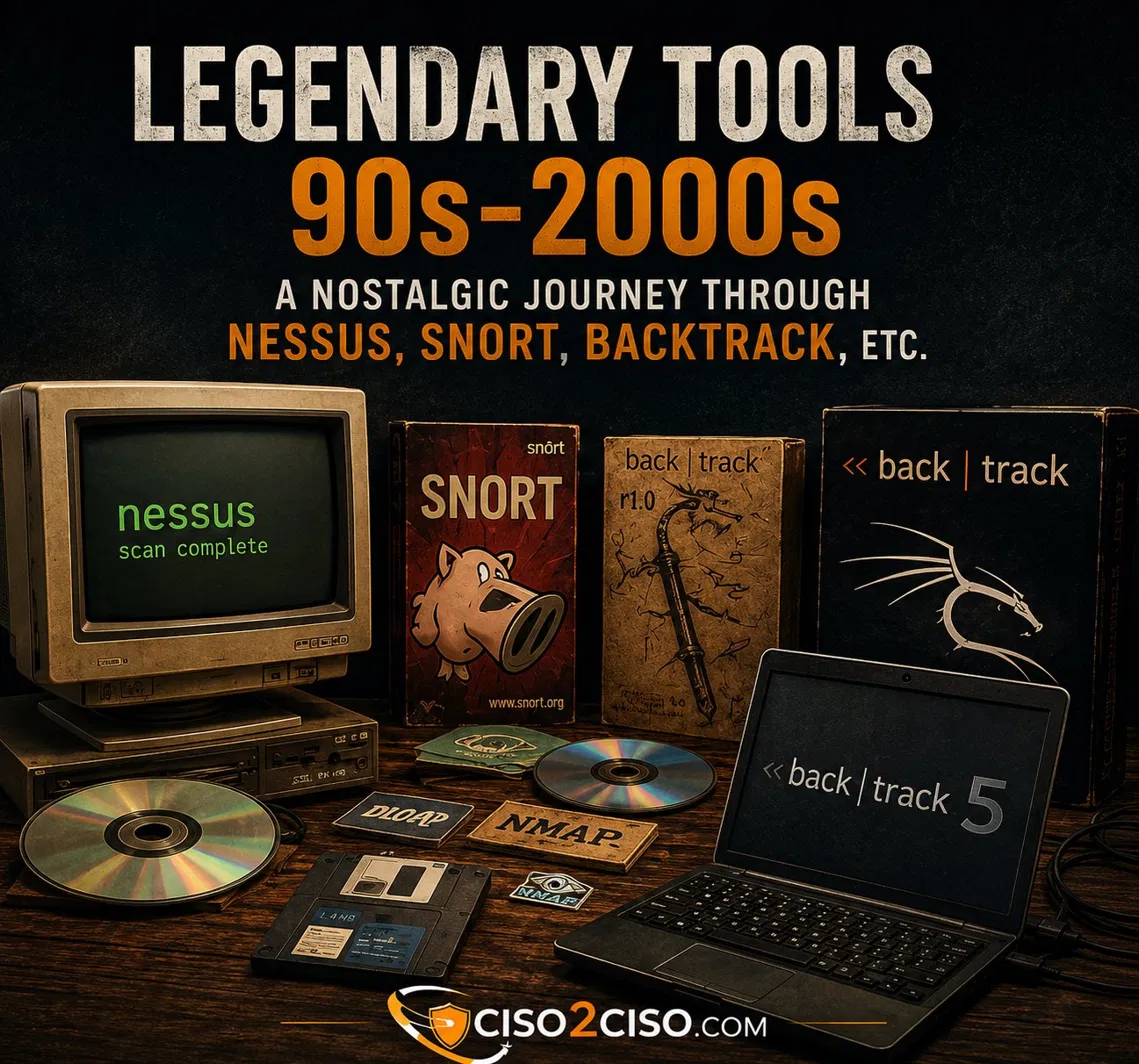
Do You Remember These Security Tools? A Nostalgic Journey Through the Tools That Forged Cybersecurity (90s–2000s)
Before EDR, XDR and cloud-native platforms, there was Nessus in open source form, Snort writing custom rules at 2am, BackTrack as our portable university, and L0phtCrack teaching us everything we needed to know about password hygiene. A tribute to the tools that educated a generation of security professionals.
Read insight →
Cyber Risk
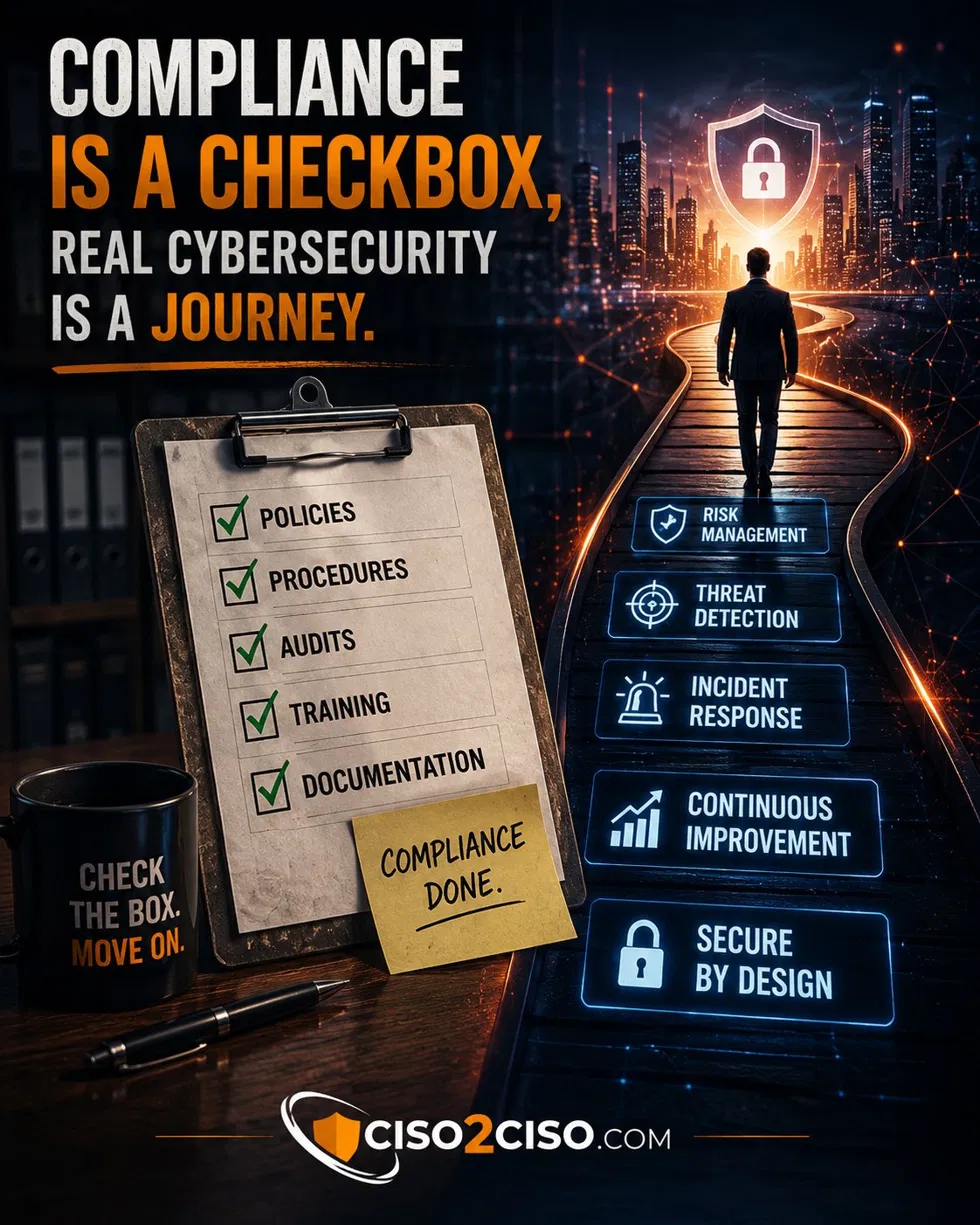
Compliance Is a Checkbox. Real Cybersecurity Is a Journey.
Achieving compliance does not equate to comprehensive security. This is not a technicality — it is one of the most dangerous misconceptions in enterprise cybersecurity. Compliance is foundational but not all-encompassing. Real security requires operational controls, automation and continuous improvement — not just passing audits.
Read insight →
Threat Intel
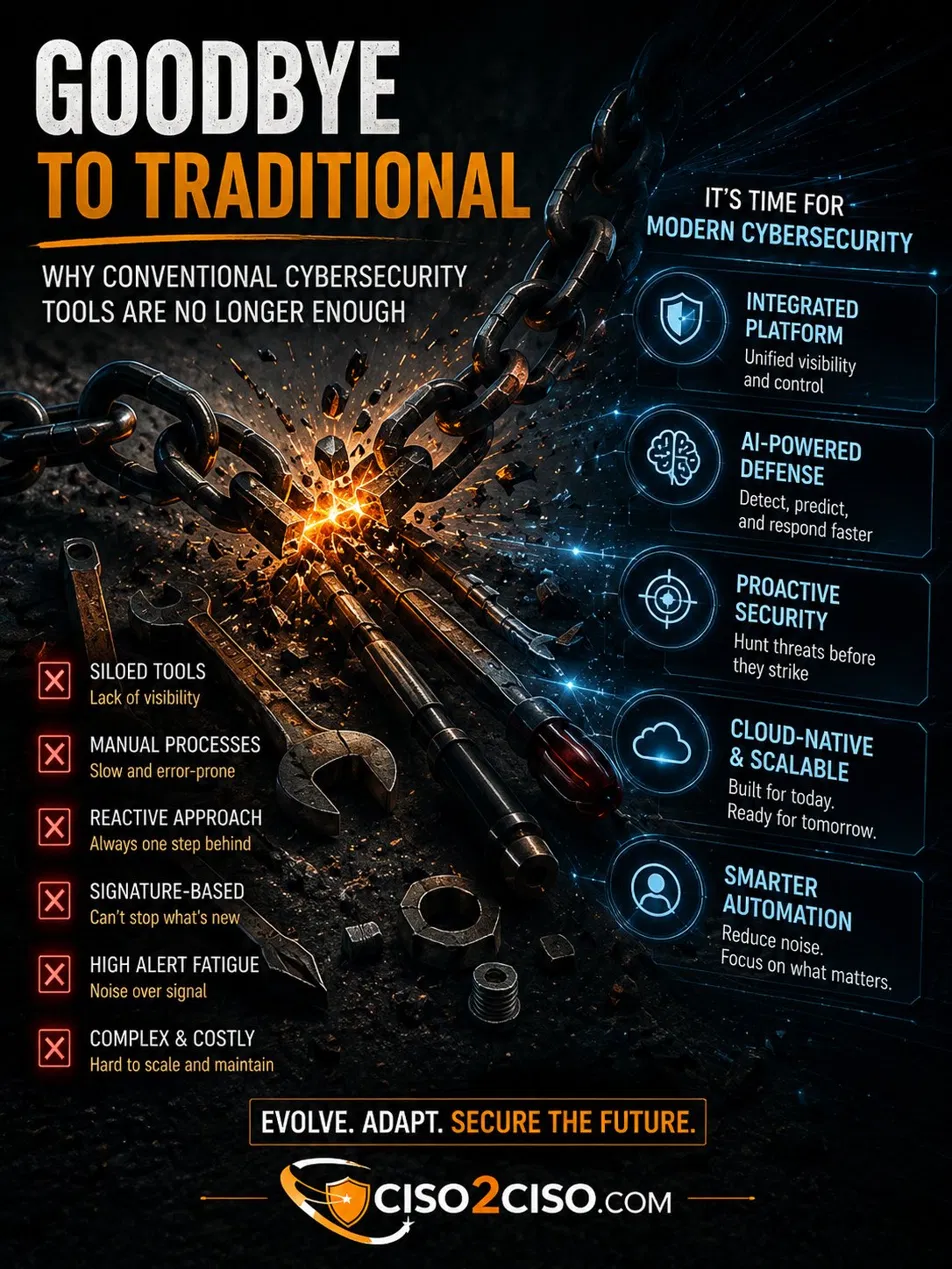
Goodbye to Traditional: Why Conventional Cybersecurity Tools Are No Longer Sufficient
As the digital threat landscape evolves in complexity, traditional cybersecurity tools — firewalls, signature-based antivirus, static SIEM rules — increasingly fail to provide adequate protection. The question is not whether to modernize. It is how to build the security architecture the current threat environment actually requires.
Read insight →
Leadership & Strategy
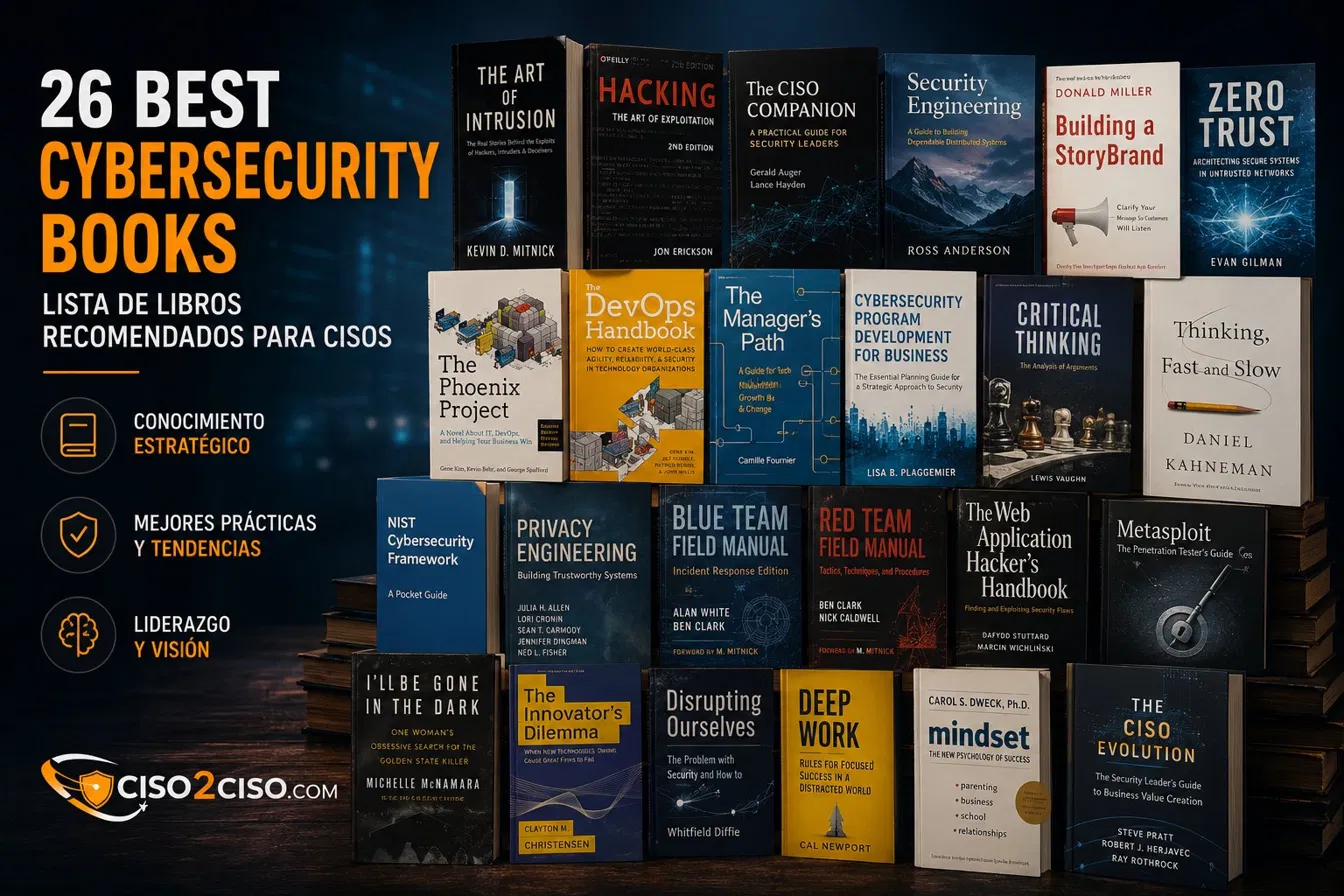
The 26 Best Cybersecurity Books Every CISO Should Read
A curated personal reading list of 26 essential cybersecurity books for CISOs and security professionals — covering ransomware defense, SOC design, security metrics, leadership, risk governance and the human dimensions of cybersecurity.
Read insight →
Board Strategy
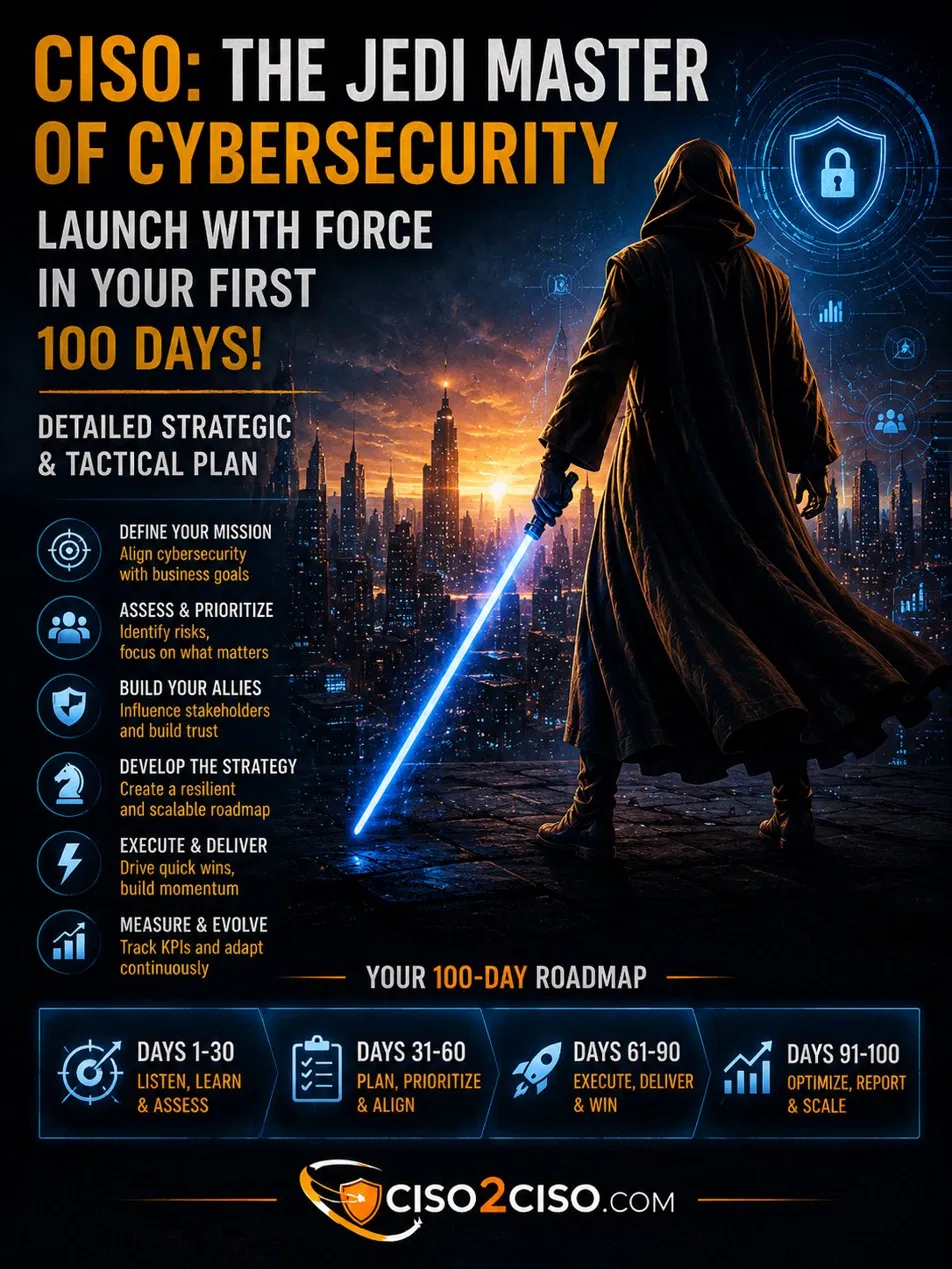
The CISO's First 100 Days: A Strategic and Tactical Playbook
The first 100 days as CISO represent a critical and unrepeatable window to establish the foundation of the security program. This strategic and tactical plan covers the four phases that take a new CISO from active listening to credible execution with visible results.
Read insight →