Editorial team
CISO2CISO Advisors Team
Research and analysis by the CISO2CISO editorial team, a community of 199K+ security leaders in 85 countries.
65 analyses
Published by the team
AI Security
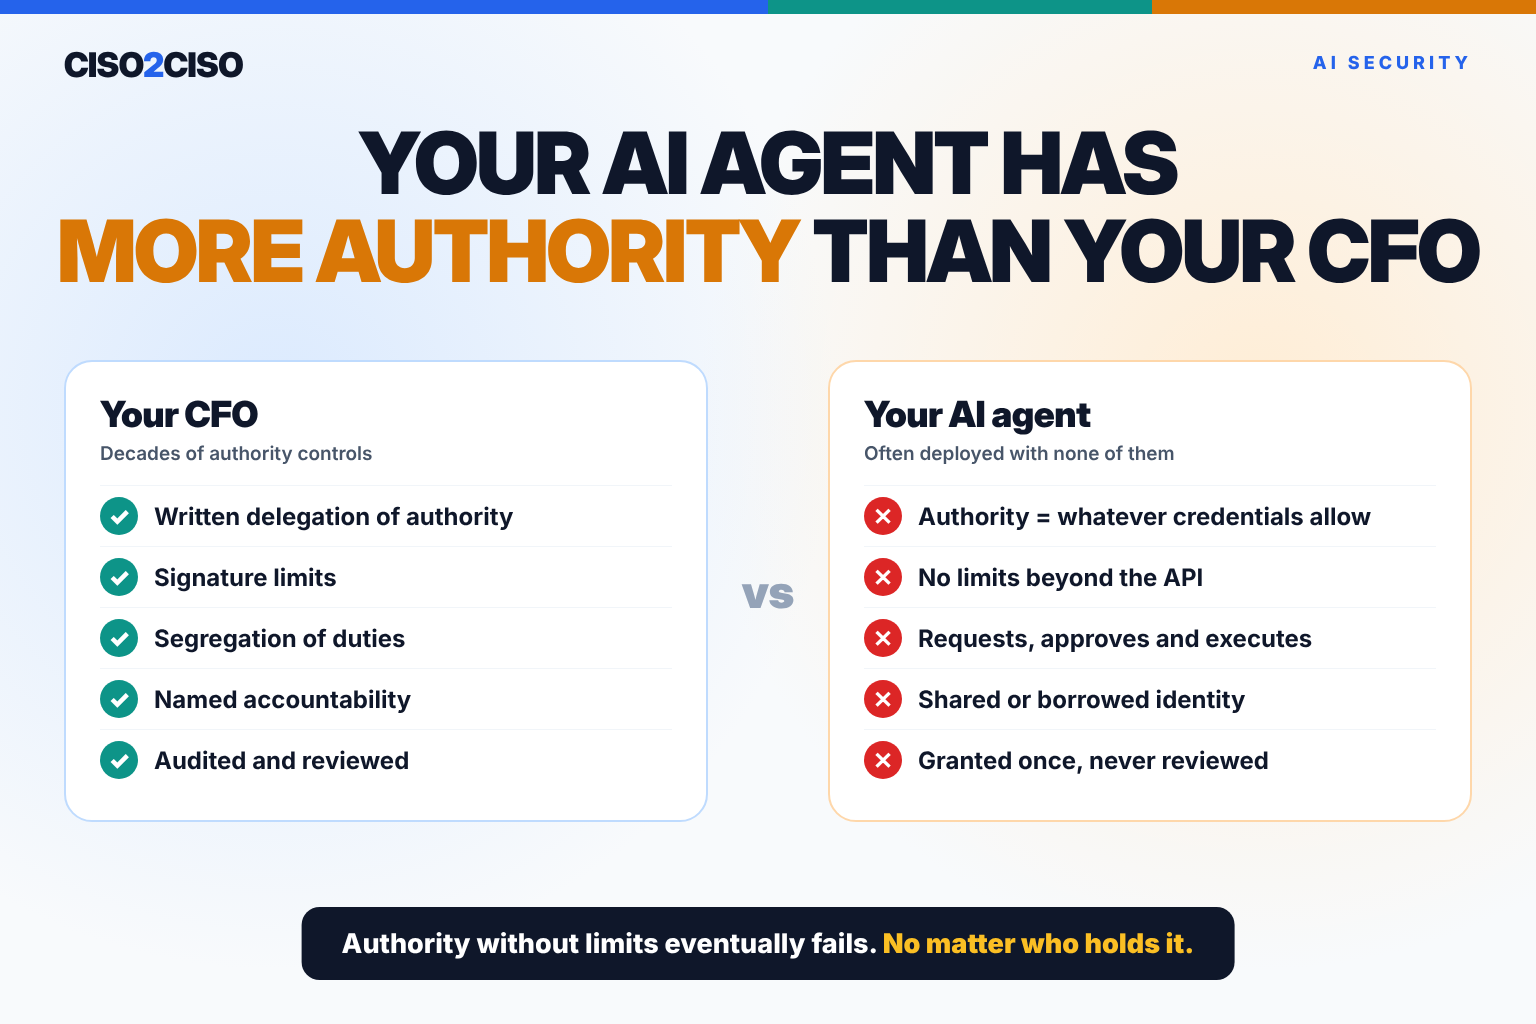
Your AI Agent Has More Authority Than Your CFO
Your CFO cannot move money without signature limits, dual approval and an audit trail. The AI agent your team deployed last quarter may be able to change records, move data and trigger payments with none of those controls. Organizations spent decades building authority controls around their most powerful people — and are now handing comparable authority to software that has no owner, no limits and no reviewer.
Read insight →
Identity Security
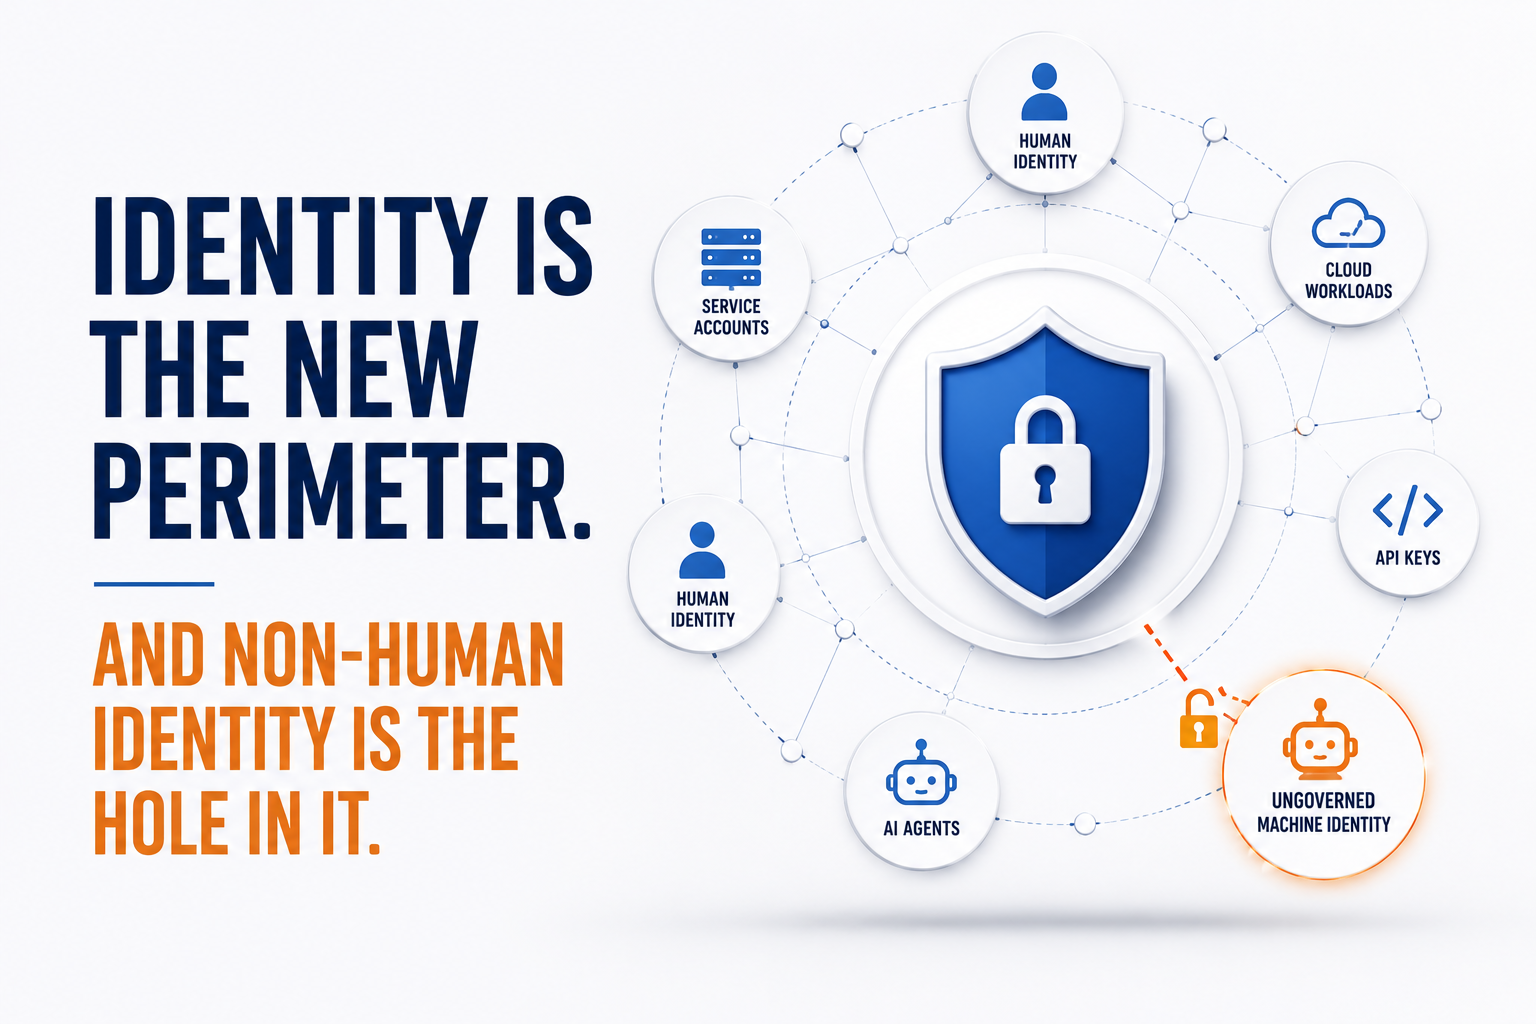
Identity Is the New Perimeter — and Non-Human Identity Is the Hole in It
Most organizations have spent a decade maturing how they govern human identity. In the same period, non-human identities — service accounts, API keys, workload and agent credentials — quietly became the majority of all identities, and almost none of that governance was extended to them. That gap is now one of the highest-priority risks in the enterprise.
Read insight →
Board Strategy
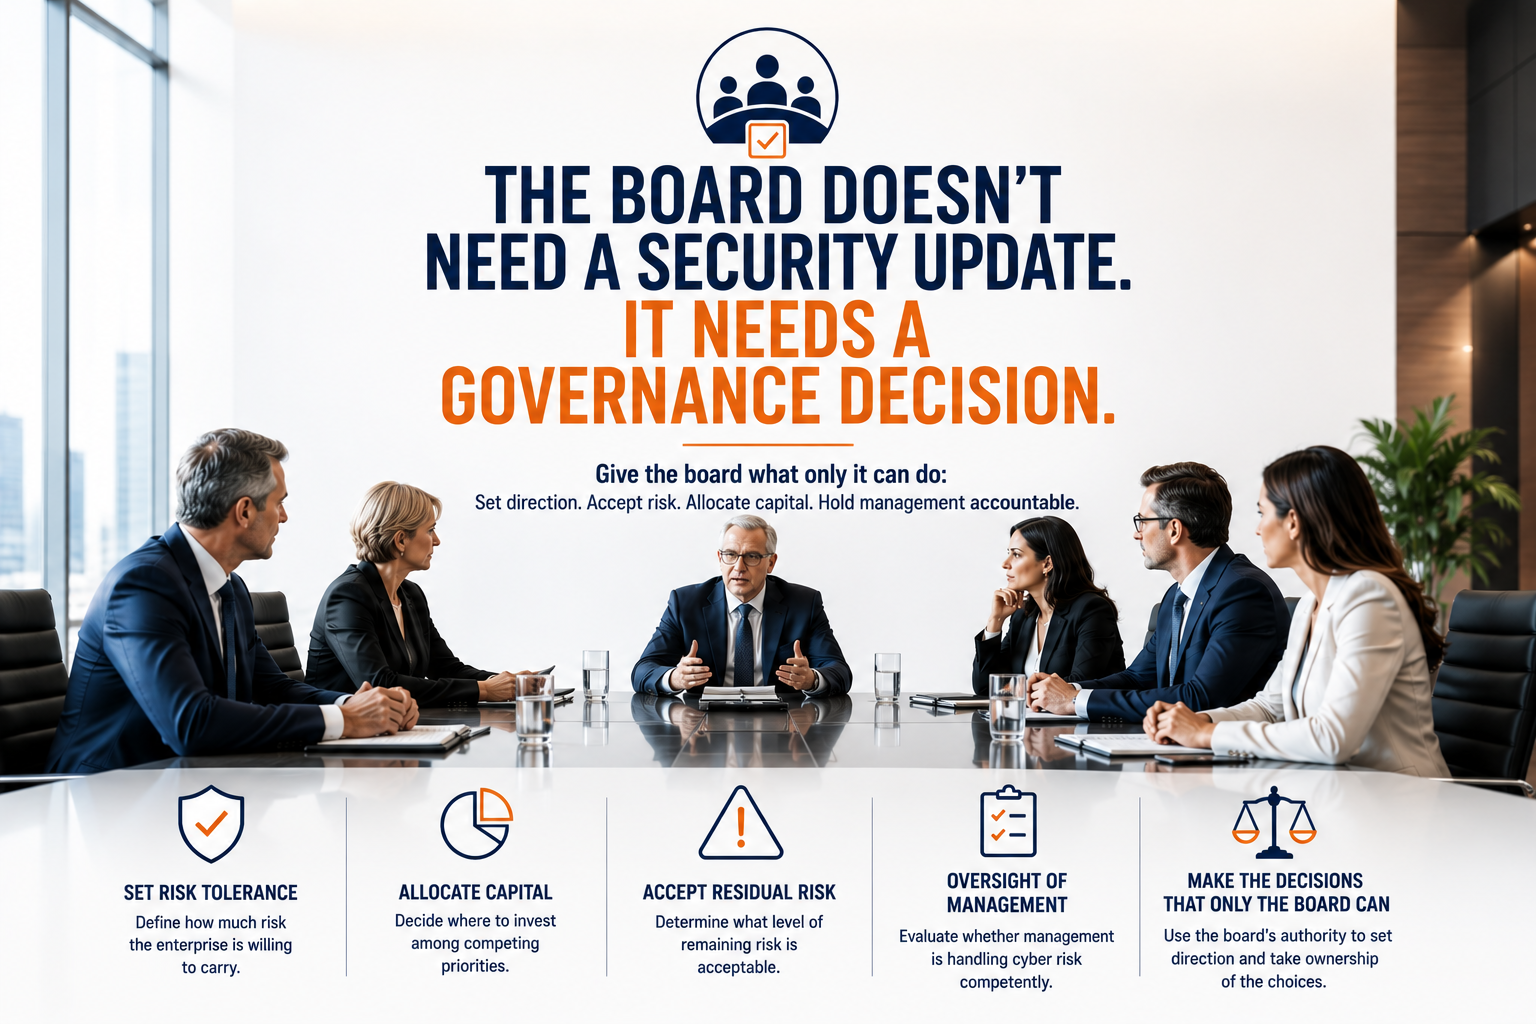
The Board Doesn't Need a Security Update. It Needs a Governance Decision.
Most CISO board presentations are status reports dressed as governance — activity, metrics and reassurance delivered to a body whose actual job is to make decisions. The shift from reporting to the board to enabling the board to govern is one of the highest-leverage changes a security leader can make.
Read insight →
Cloud Security
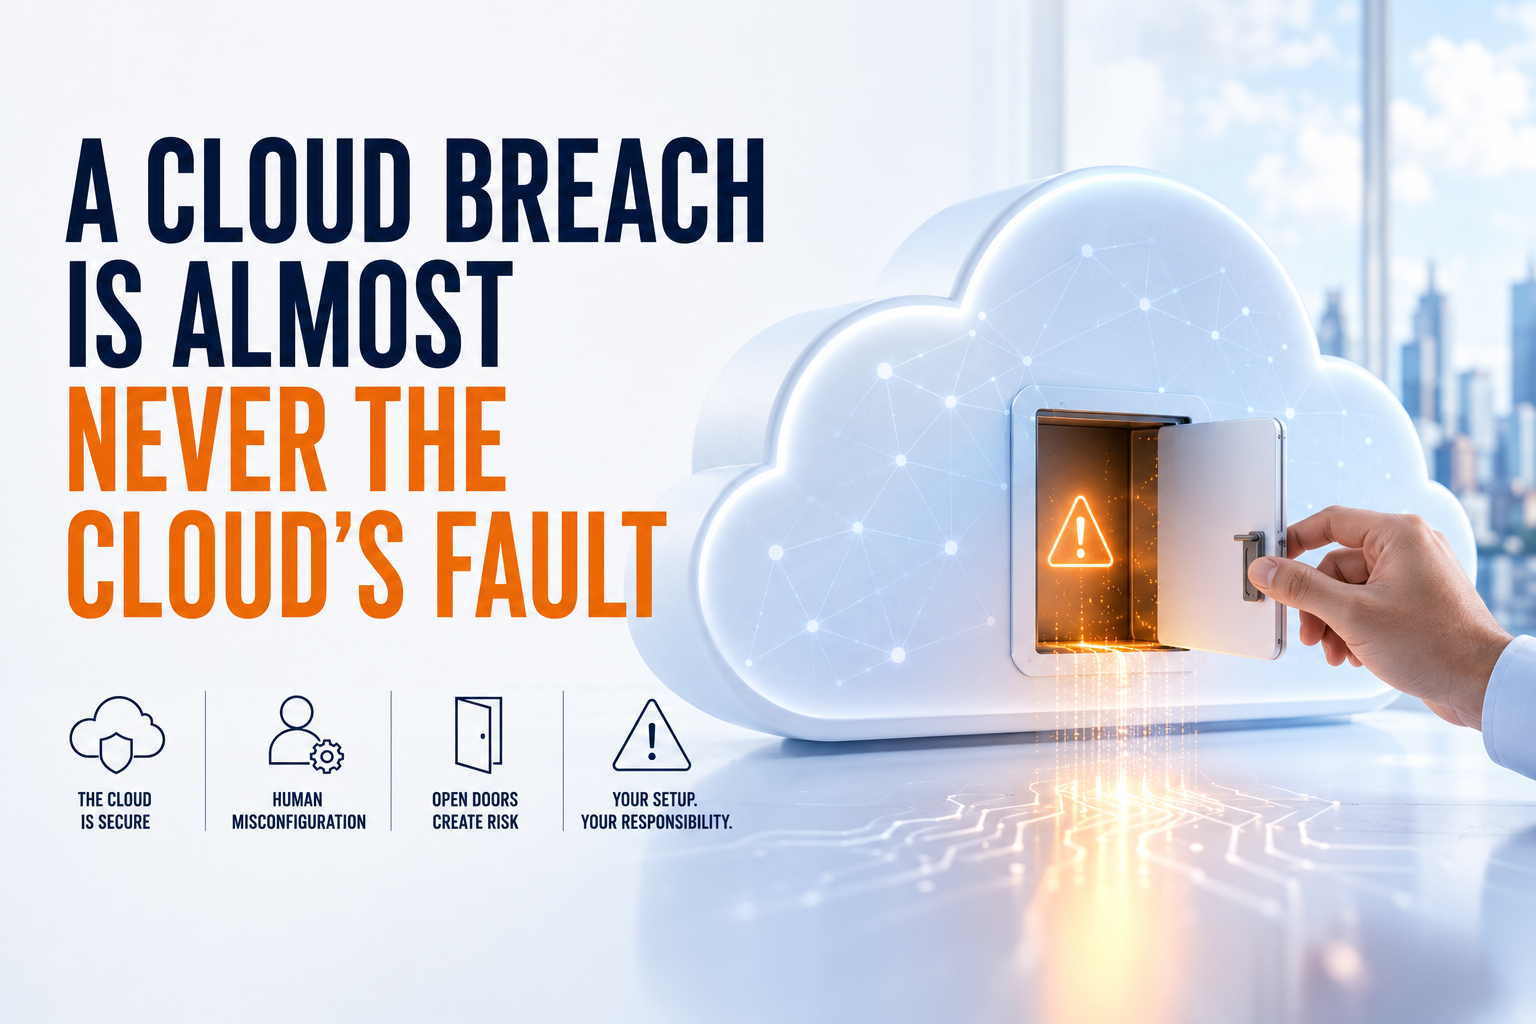
The Cloud Breach Is Almost Never the Cloud's Fault
The dominant cause of cloud incidents is not a failure of the cloud provider. It is the organization's own configuration, identity and architecture decisions operating exactly as instructed. Securing the cloud is less about defending a perimeter and more about governing the decisions that determine what is exposed.
Read insight →
SASE
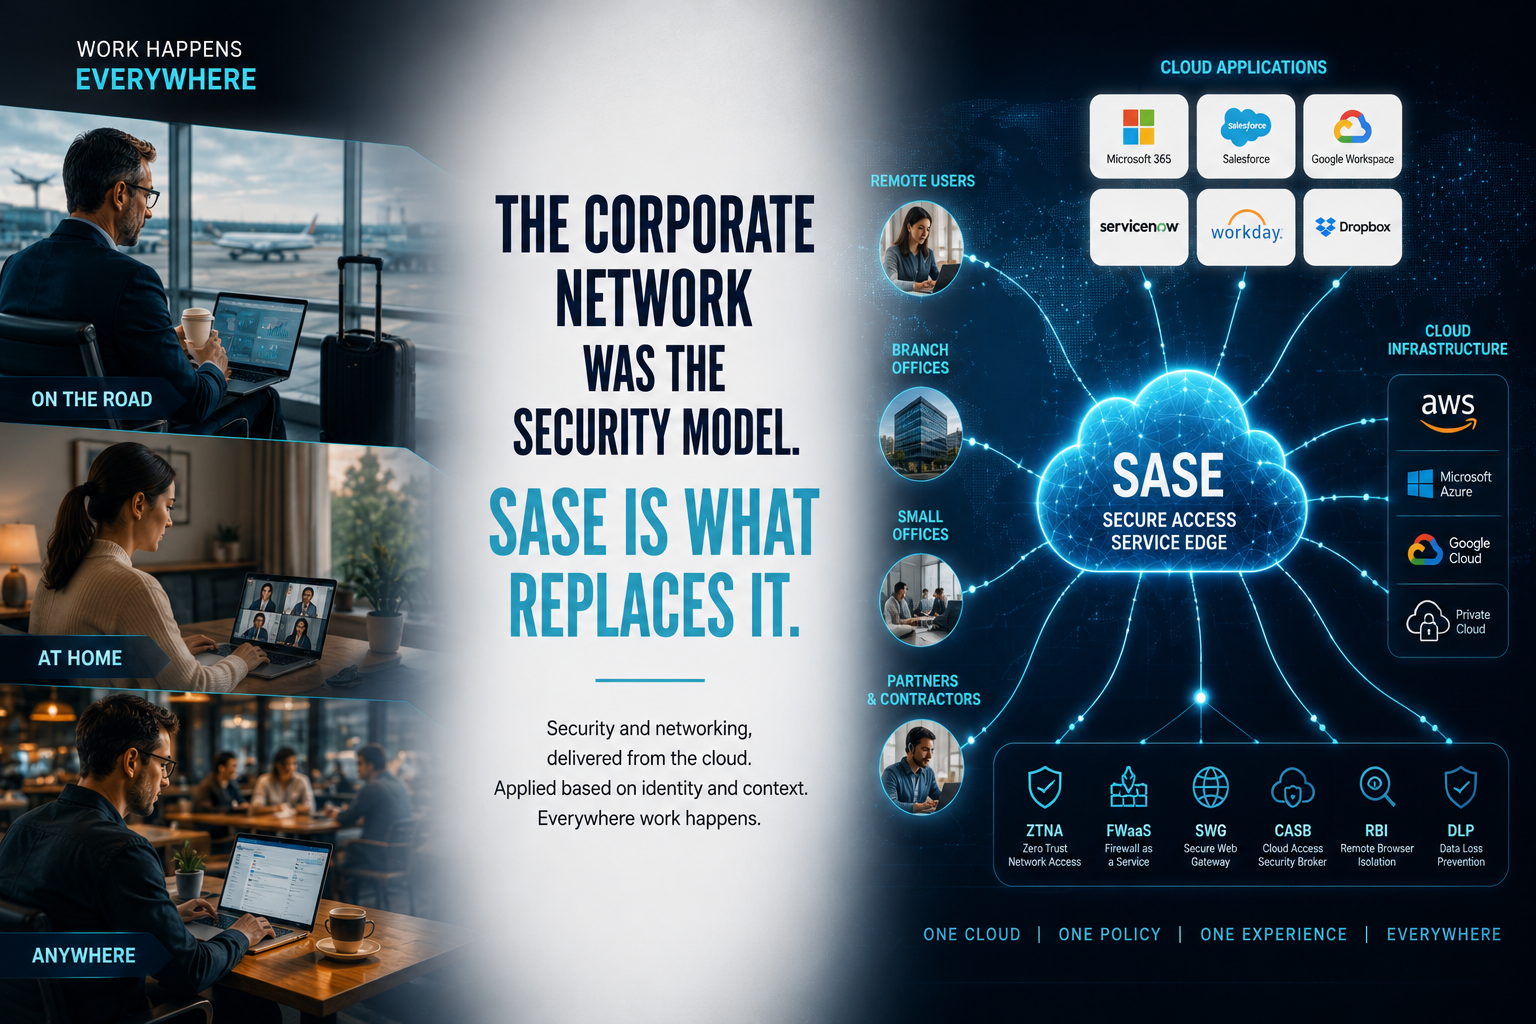
The Corporate Network Was the Security Model. SASE Is What Replaces It.
For decades, security was a function of where you were — inside the corporate network meant trusted, outside meant not. That model died when the users, the applications and the data all left the network. SASE is the architecture that replaces location-based security with identity- and context-based security, delivered from the cloud.
Read insight →
Events
The Cybersecurity Events Worth the Flight: A Curated Global Guide to 2026–2027
A deep, curated, region-by-region guide to the cybersecurity events that actually move the industry — from board-level summits to hardcore technical gatherings — across the rest of 2026 and all of 2027. It covers the global flagships and the local scenes that matter, with special depth on Spain, the UK, Brazil, Argentina and the wider Latin American community. Each event includes dates, location, a sharp brief, the recommended audience, and whether it is built for executives, practitioners, or both.
Read insight →
Data Security
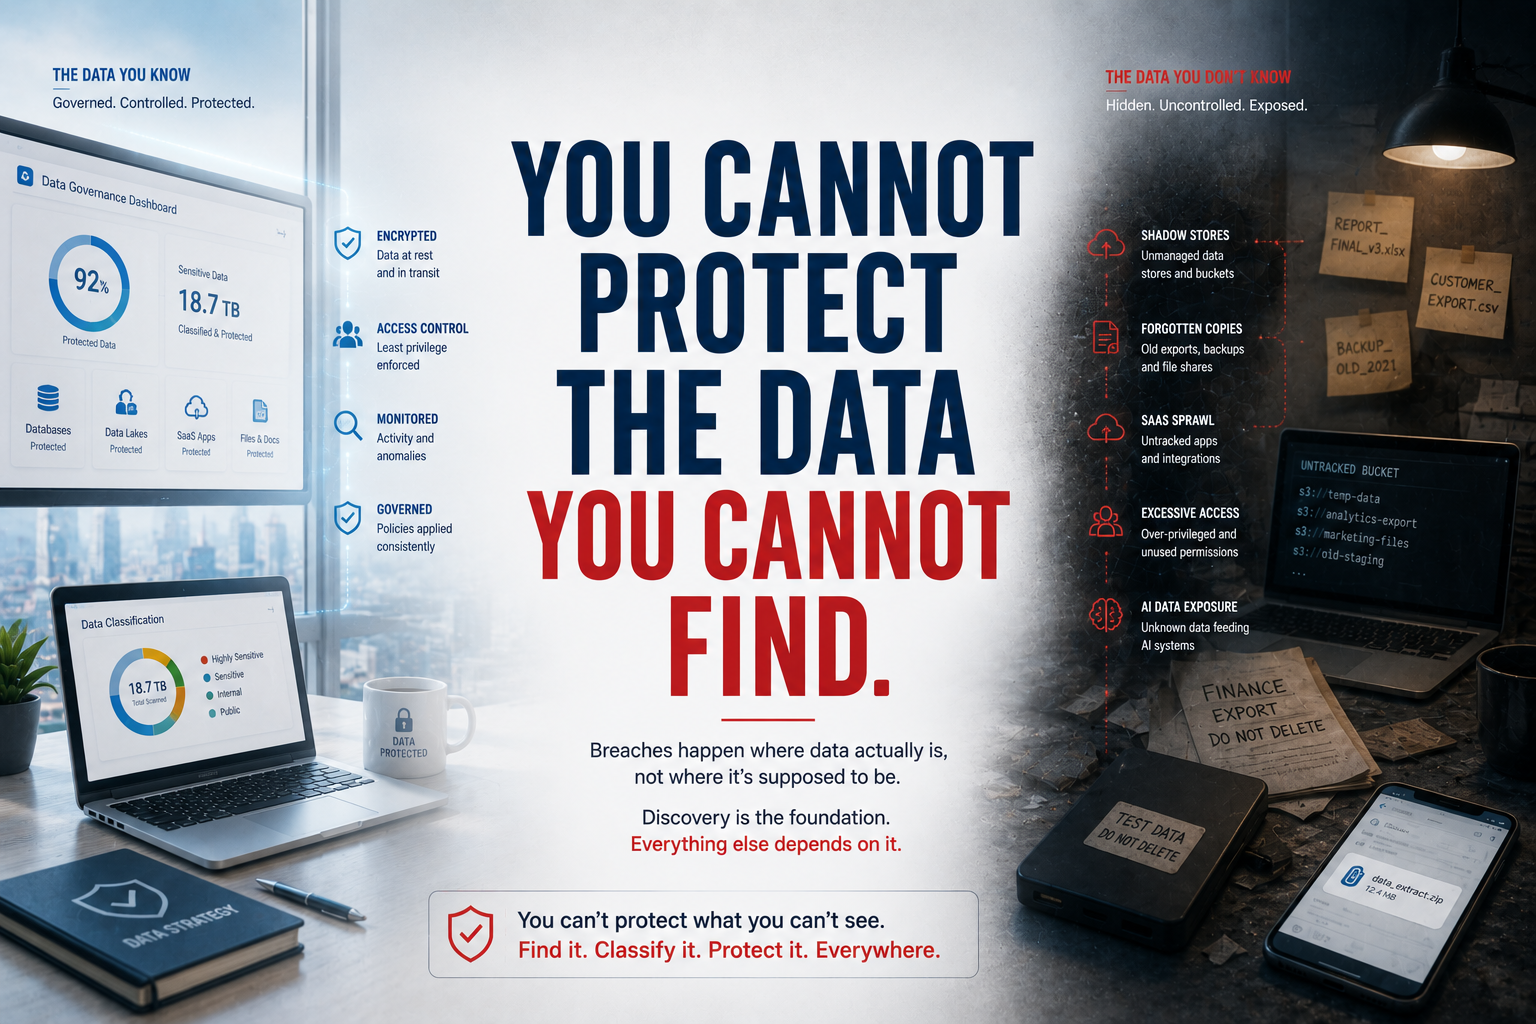
You Cannot Protect the Data You Cannot Find
Most data security programs protect the places data is supposed to be. The breaches happen where data actually is — in the copies, exports, shadow stores and forgotten repositories no one mapped. And as AI systems consume enterprise data at unprecedented scale, the cost of not knowing where your data lives has never been higher.
Read insight →
Zero Trust
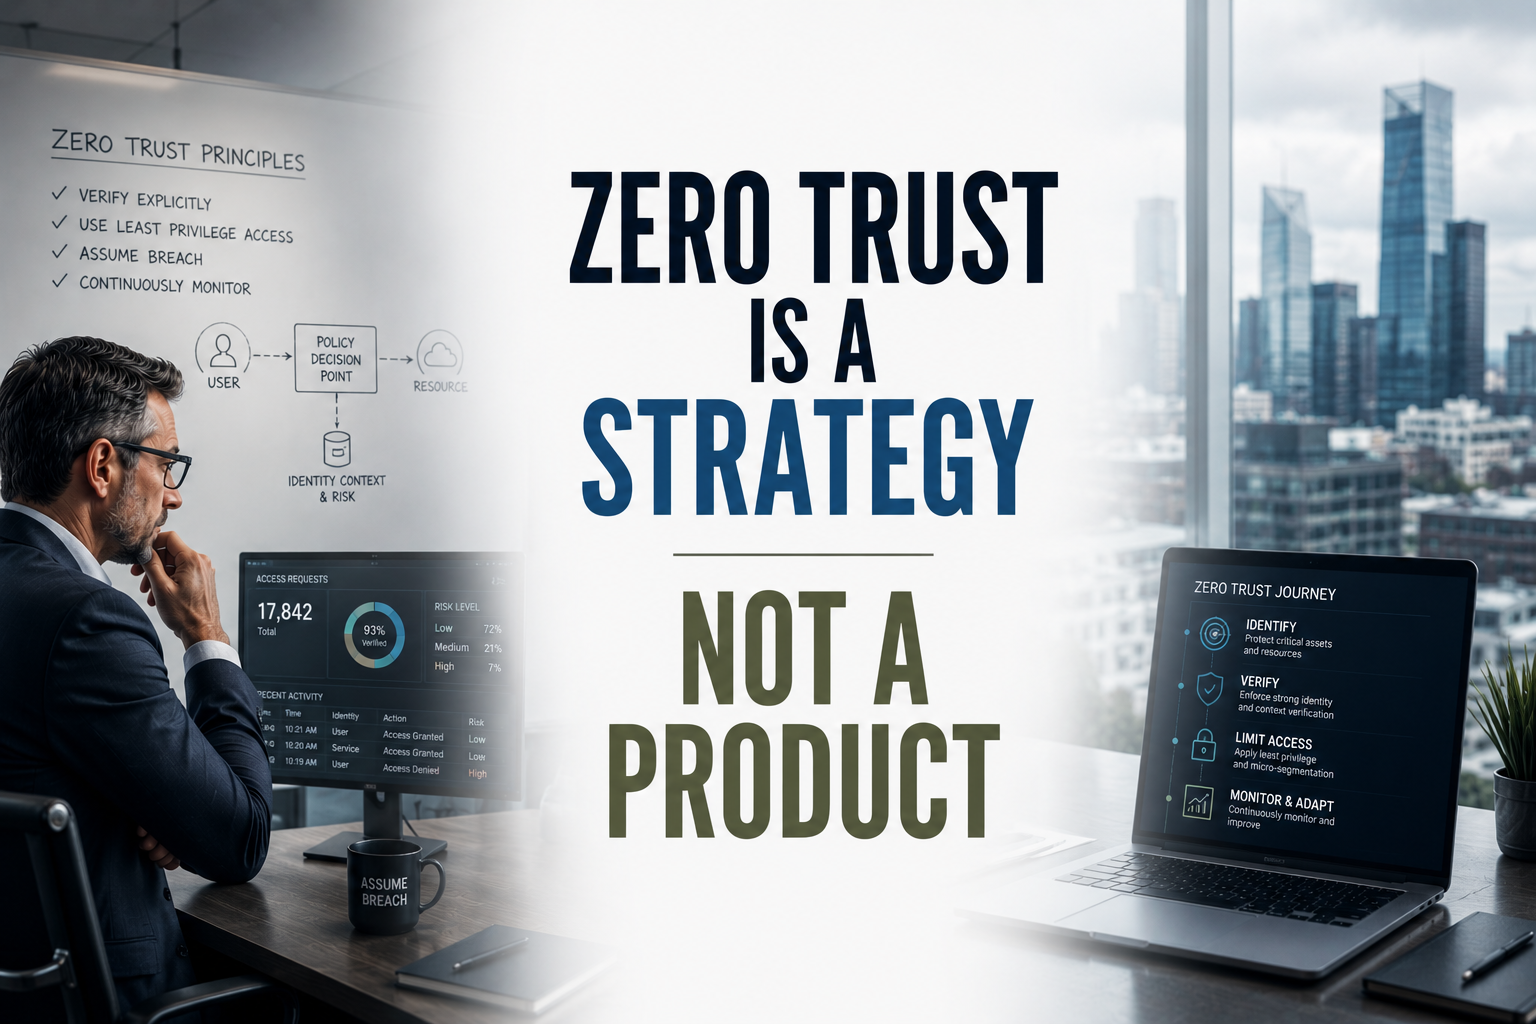
Zero Trust Is a Strategy. You Have Been Sold a Product.
Zero Trust has been packaged, branded and sold as something you can purchase and deploy. It is none of those things. It is an architectural strategy and an operating discipline that no single product can deliver — and confusing the two is why so many Zero Trust initiatives stall after the procurement.
Read insight →
AI Security
The AI Security Gap No Policy Can Close
Most organizations have an AI policy. Far fewer have AI security. The gap between the two is where the real risk lives — and it can only be closed by treating AI security as an operating discipline with inventory, ownership, controls and evidence, not as a document that lives on the intranet.
Read insight →
Board Strategy
The CISO Is Now Personally on the Hook. Here's What That Changes.
A series of high-profile cases has established that security leaders can face personal legal and professional consequences for how they handle incidents and what they tell — or fail to tell — their organizations and regulators. This changes the CISO role in ways that extend well beyond the individual, reshaping the relationship between the security leader, the board and the truth.
Read insight →
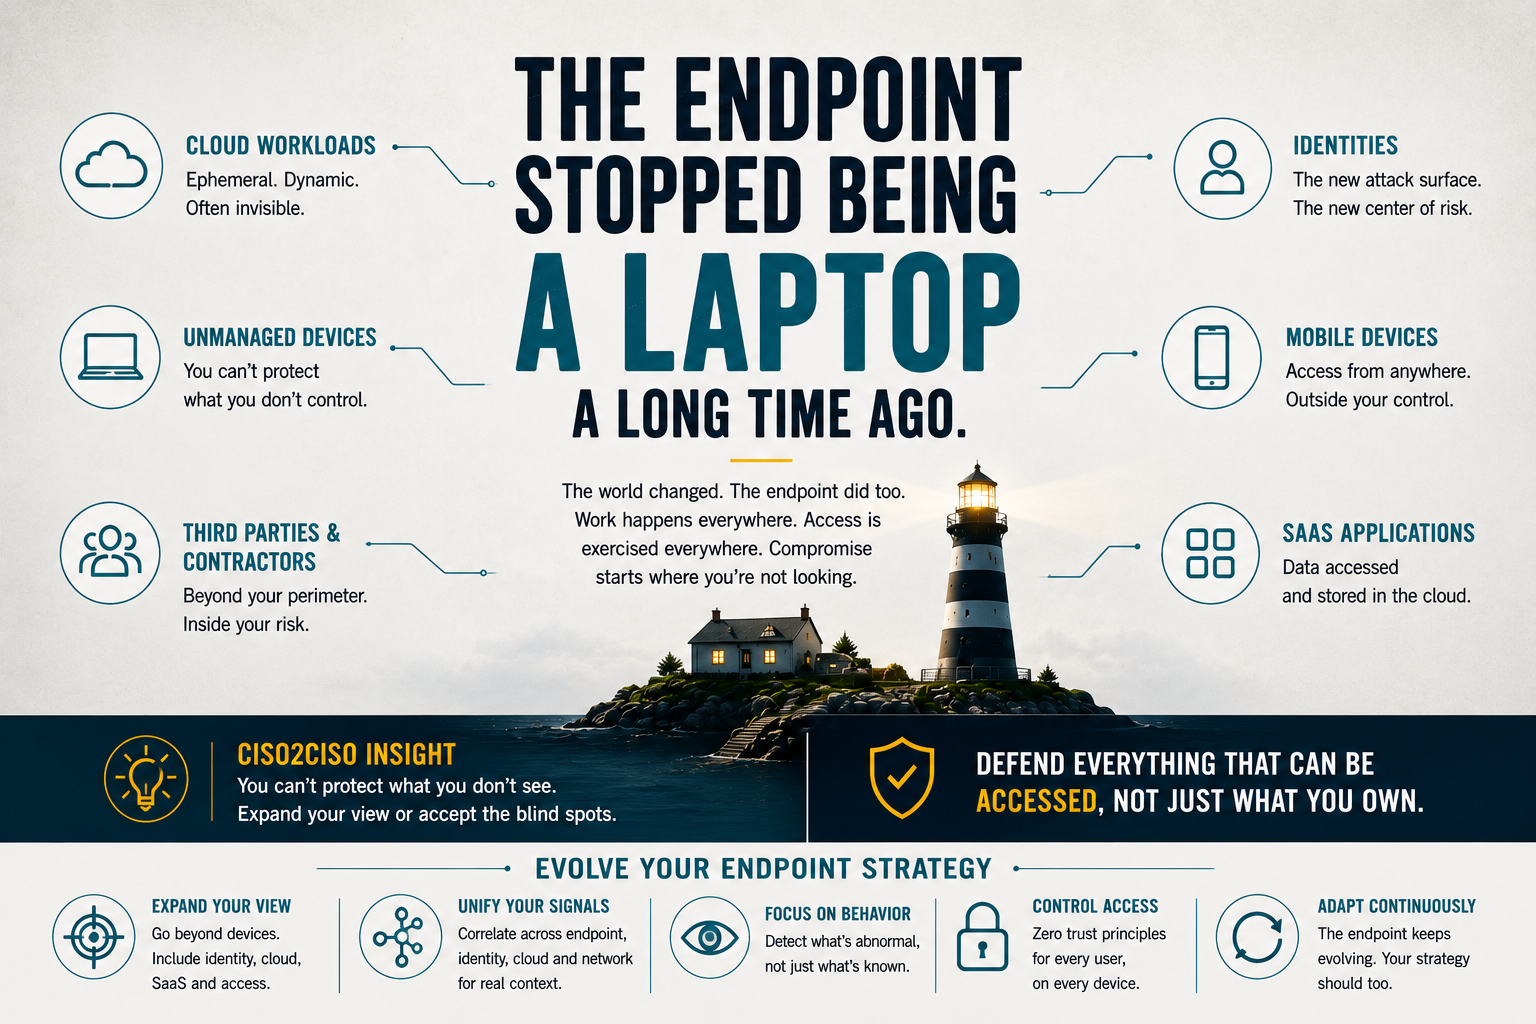
Endpoint Security
The Endpoint Stopped Being a Laptop a Long Time Ago
Endpoint security still conjures the image of a managed laptop with an agent on it. But the endpoint has fragmented into cloud workloads, mobile devices, identities and unmanaged hardware — and a strategy anchored to the laptop is defending a shrinking fraction of where compromise actually begins.
Read insight →
OT Security
The Network That Runs the Plant Was Never Built to Be Defended
Operational technology was engineered for availability and safety over decades — long before anyone imagined it would be connected, targeted and held to ransom. Securing it is not a matter of porting IT security into the plant. It requires a different model that respects what the environment was actually built to do.
Read insight →
Cyber Risk
The Risk Heat Map Is Where Accountability Goes to Die
The red-amber-green heat map has become the default language of cyber risk reporting — and it is precisely why so many boards cannot make decisions about it. Quantifying cyber risk in business and financial terms is not a nice-to-have. It is the difference between a risk function that informs decisions and one that decorates slides.
Read insight →
Threat Intel
Threat Intelligence That Doesn't Change a Decision Is Just Expensive News
Many organizations consume enormous volumes of threat intelligence and act on almost none of it. The value of intelligence is not in how much you collect — it is in whether it changes what you decide and do. Most threat intel programs are libraries of unread reports, not engines of better decisions.
Read insight →
API Security
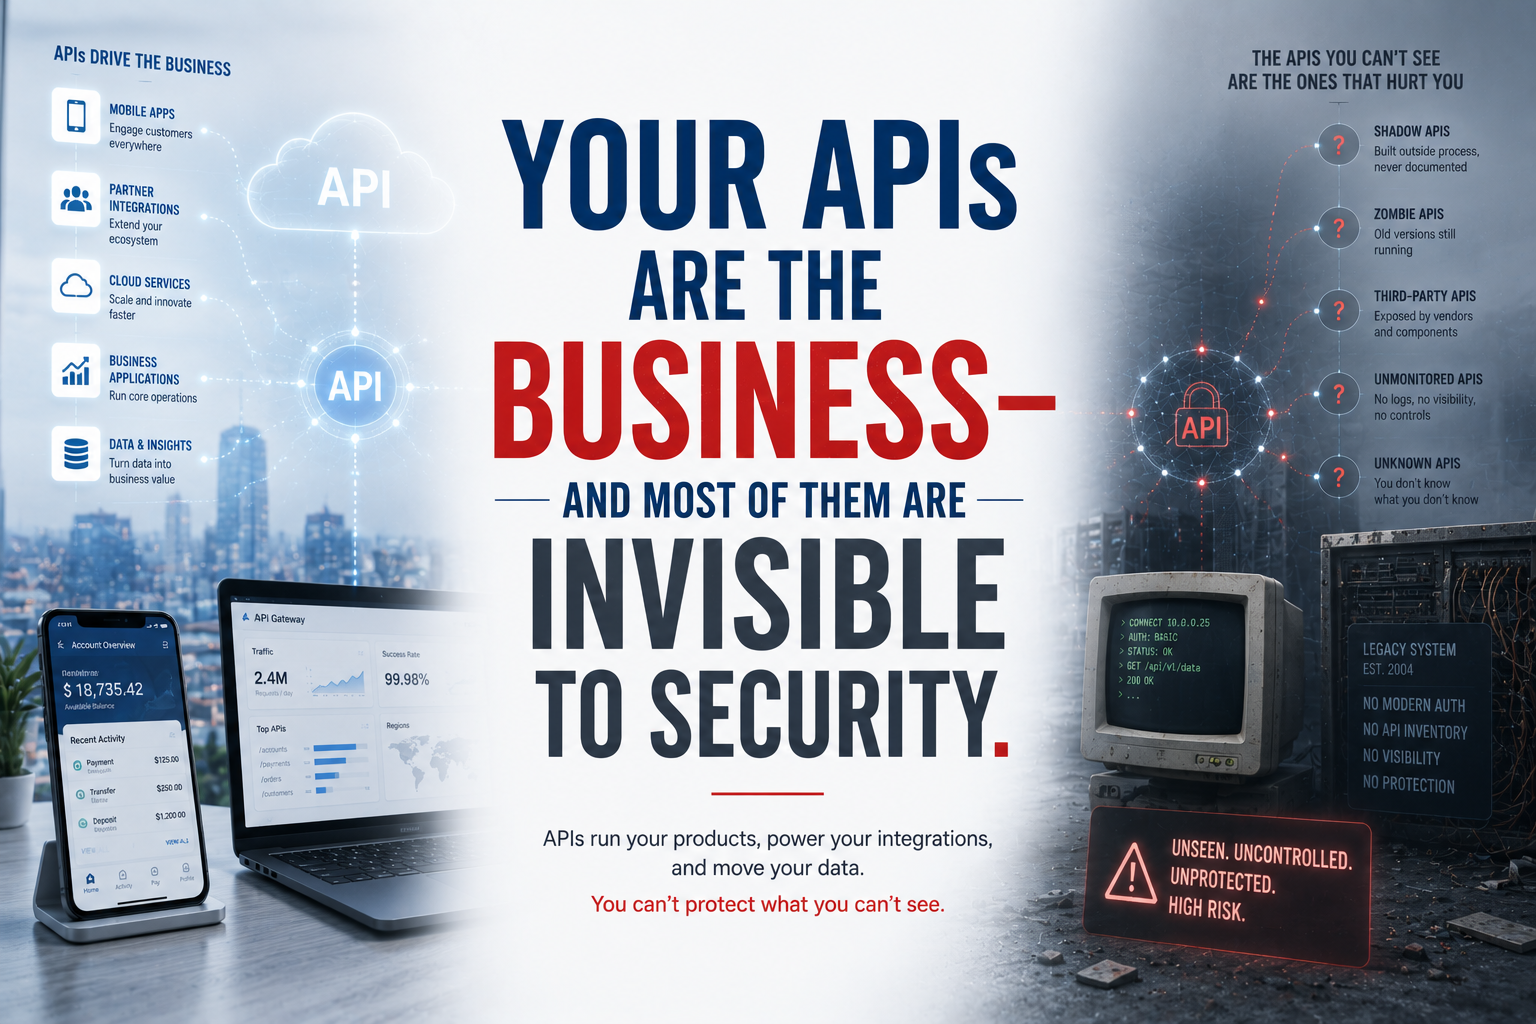
Your APIs Are the Business — and Most of Them Are Invisible to Security
APIs are no longer plumbing connecting systems — they are how the business itself operates, exposes value, and moves data. Yet most organizations cannot produce an accurate inventory of the APIs they run, and the traditional tools meant to protect them were built for a different kind of attack. The gap between API reliance and API visibility is one of the most exposed surfaces in the modern enterprise.
Read insight →
OT Security
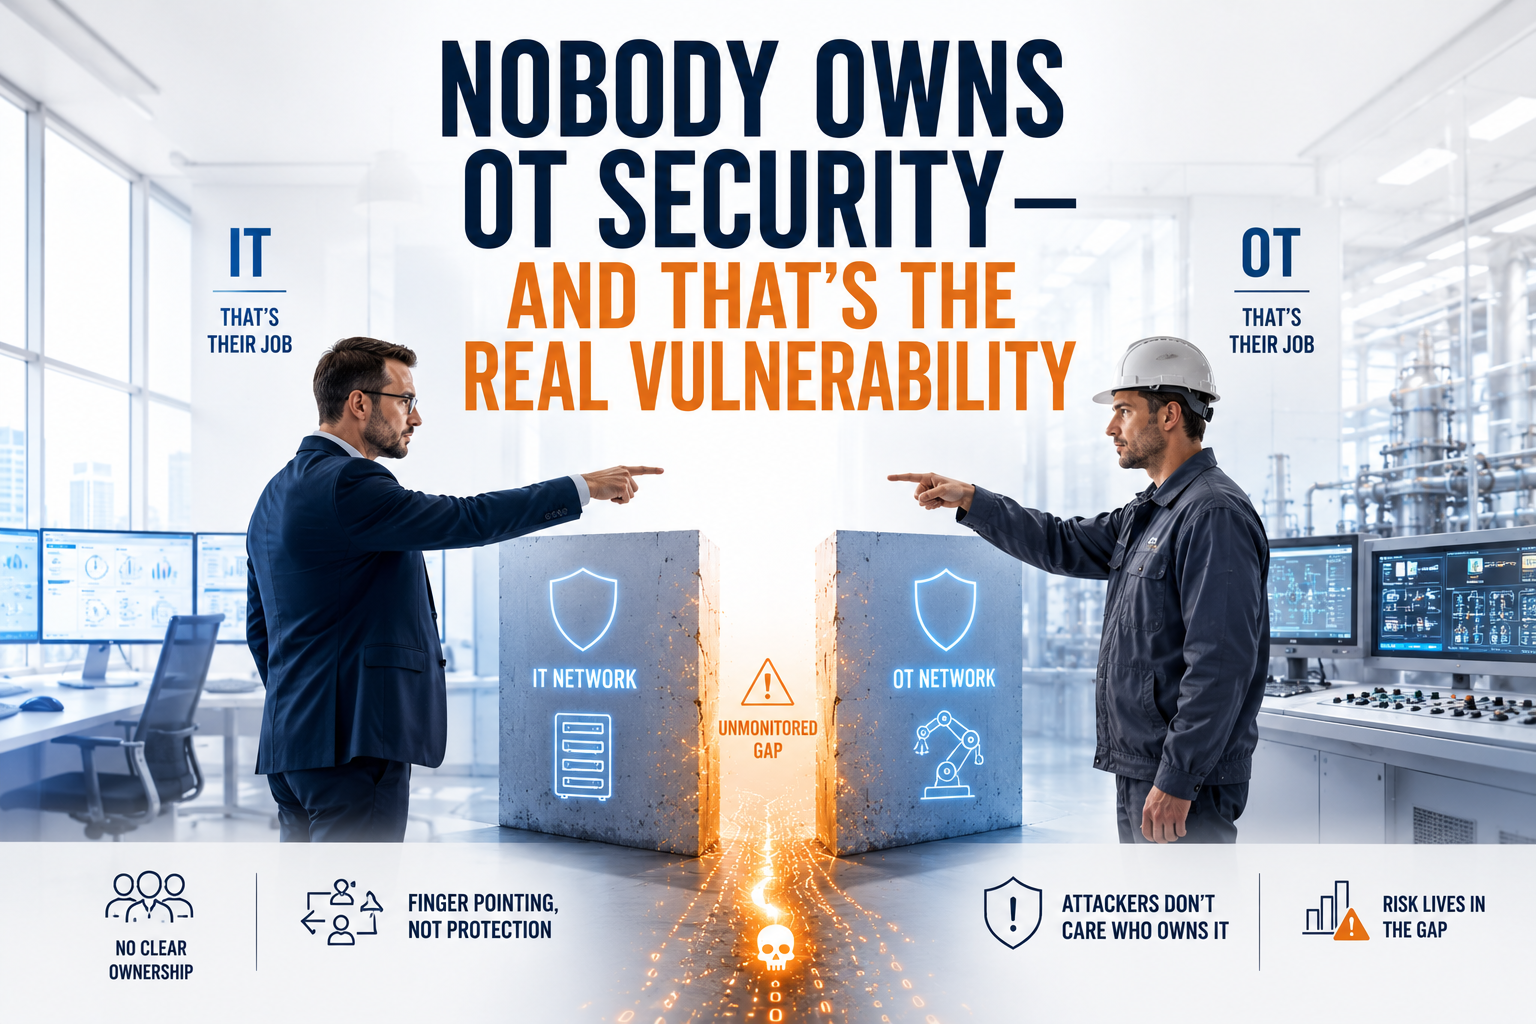
Nobody Owns OT Security — and That's the Real Vulnerability
The most dangerous gap in most industrial environments is not technical. It is organizational: operational technology security falls between the security team, the operations team and the engineers who run the plant, owned fully by none of them. Until accountability is resolved, no amount of tooling will close the gap.
Read insight →
AI Security
Prompt Injection Is the Vulnerability Class We Don't Know How to Fix Yet
Traditional vulnerabilities have patches. Prompt injection does not — it exploits the fact that AI systems cannot reliably separate trusted instructions from untrusted data. As organizations connect AI agents to real tools and data, this unsolved vulnerability class is quietly becoming one of the most consequential exposures in the enterprise.
Read insight →
Board Strategy
The Hardest Question a CISO Faces: Could This Happen to Us?
A major ransomware incident hits the news. Ten minutes later the message arrives — the Board wants to see you. Someone asks the question every CISO dreads. This is not a technical question. It is an existential one. And the way you answer it says far more than you think.
Read insight →
Zero Trust
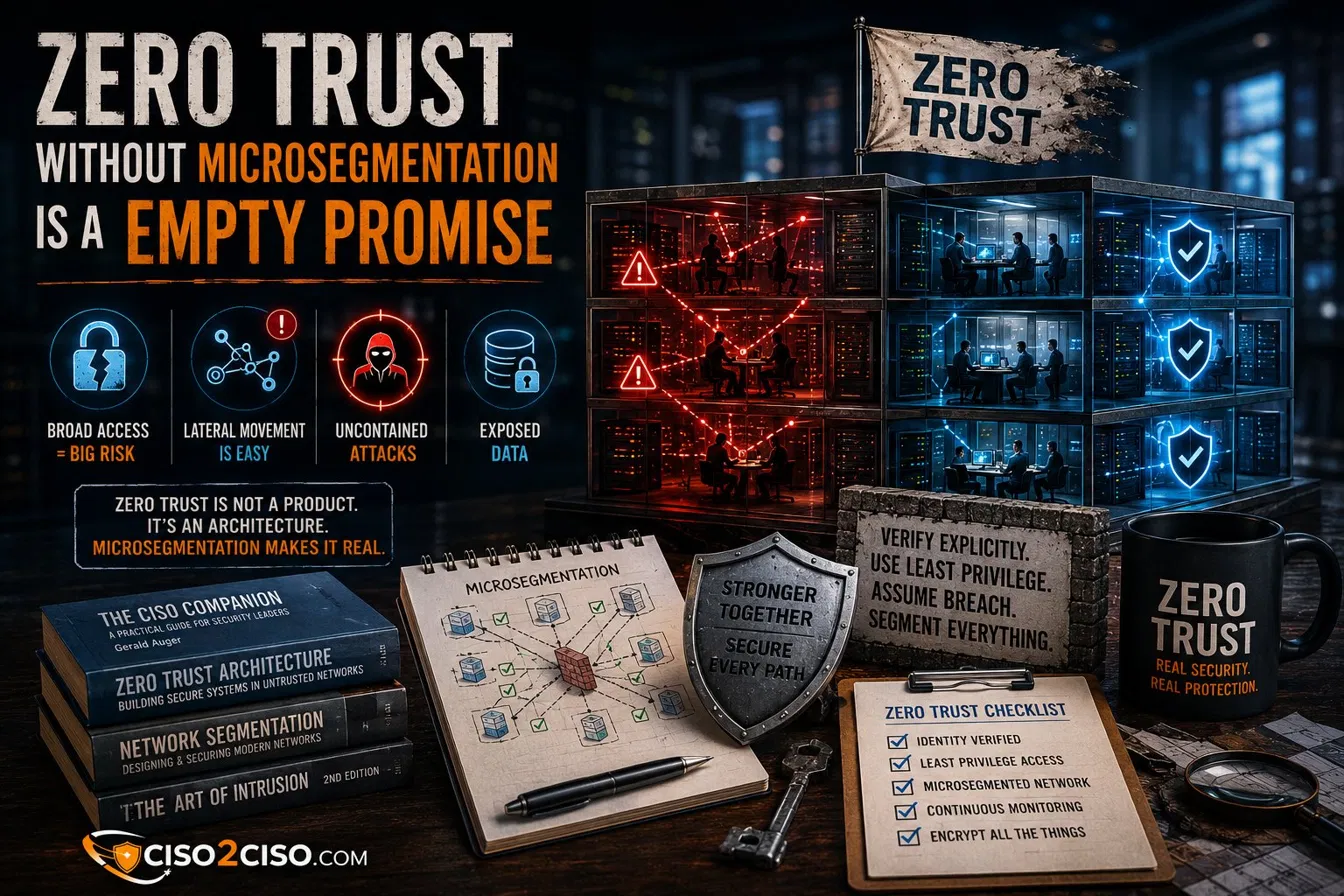
Without Microsegmentation, Zero Trust Is an Empty Promise
Modern attackers no longer break through the front door — they move laterally, silently and deliberately. Without microsegmentation, they have a free corridor through your entire environment. With it, they hit electrified walls at every turn.
Read insight →
Cyber Risk
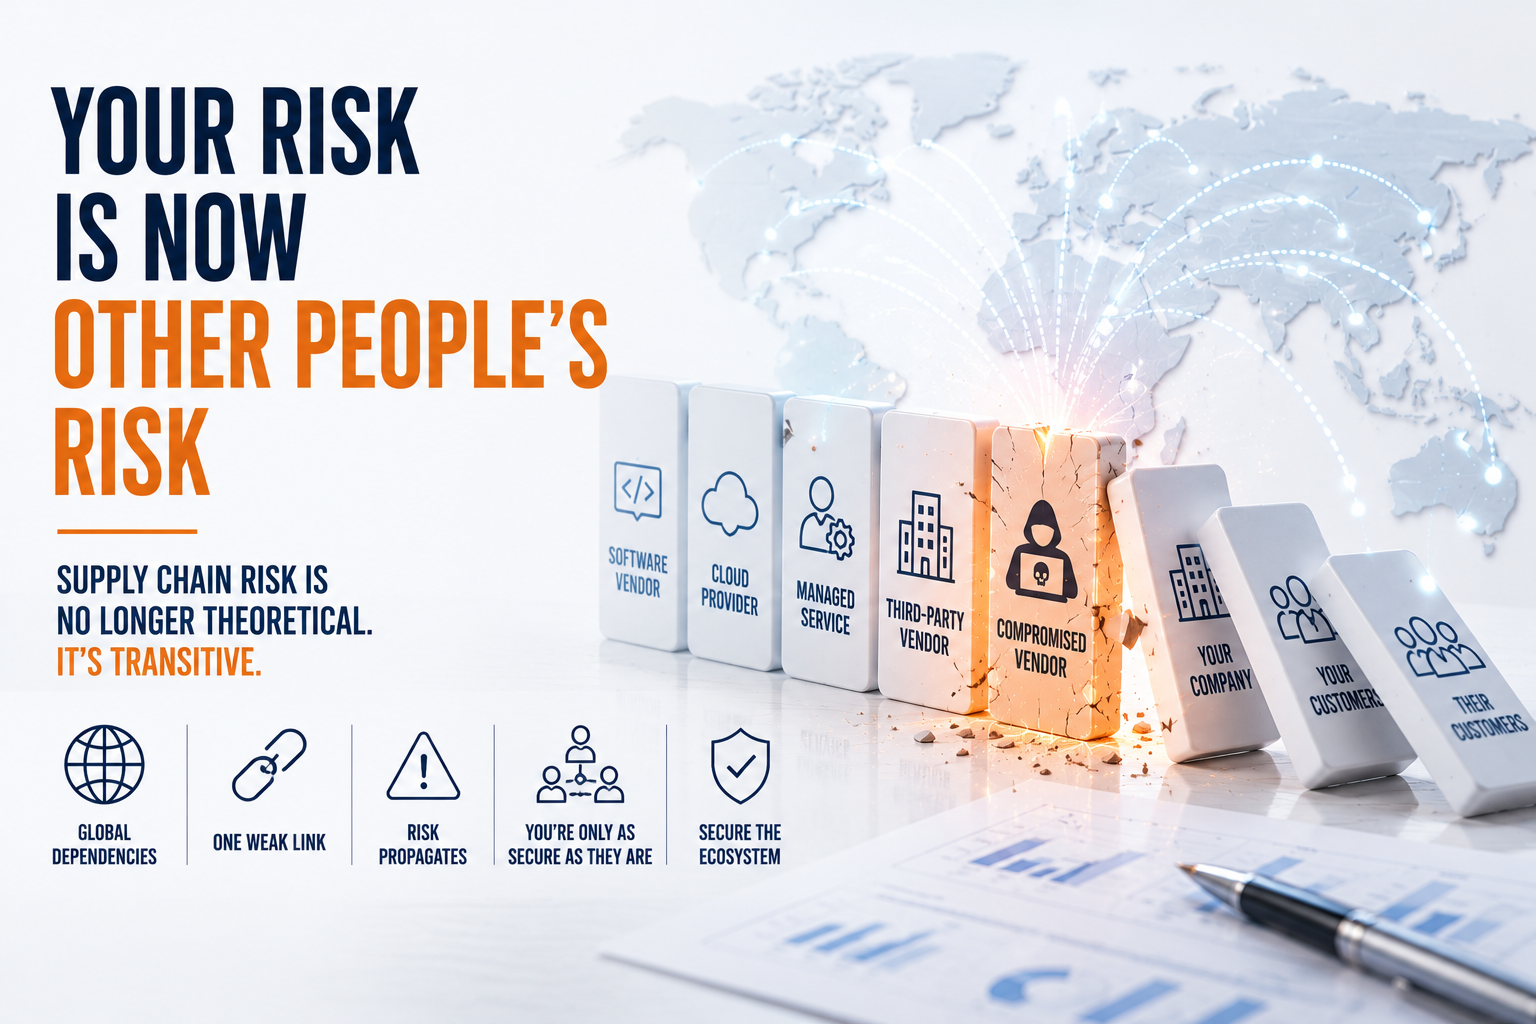
Your Risk Is Now Other People's Risk: The Third-Party Problem
A growing share of an organization's cyber risk no longer lives inside the organization. It lives in the vendors, suppliers and platforms it depends on — and in the vendors those vendors depend on. Managing third-party risk with annual questionnaires was never adequate, and the concentration of digital dependence has made the gap dangerous.
Read insight →
Zero Trust
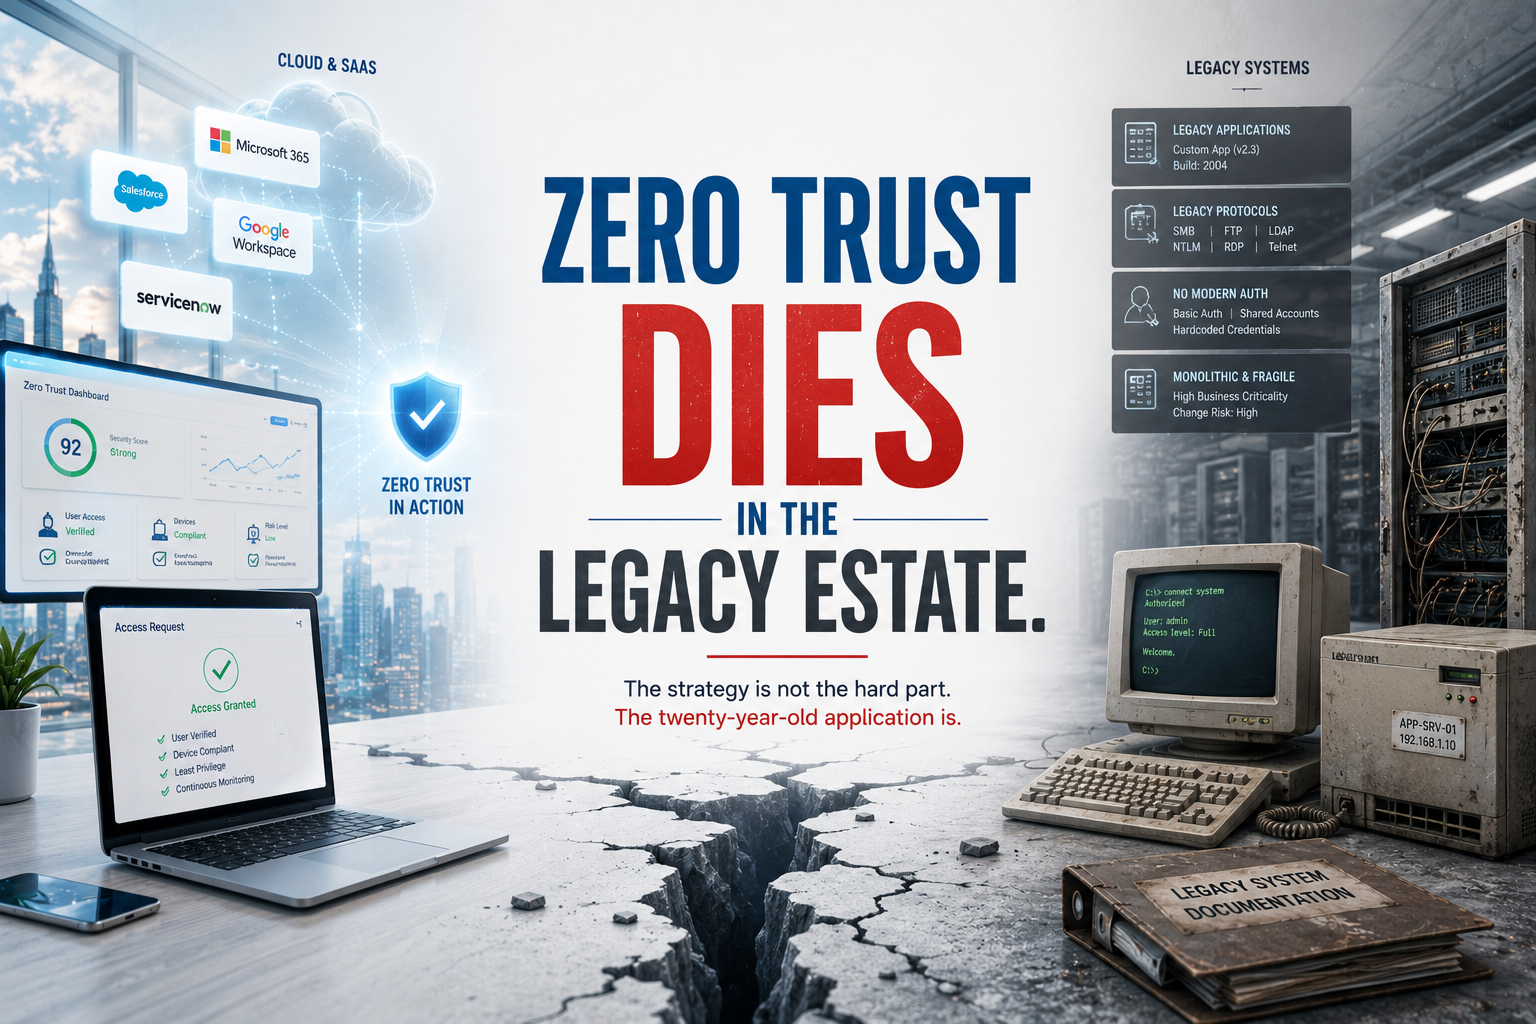
Zero Trust Dies in the Legacy Estate
Zero Trust is straightforward to apply to modern, cloud-native systems built with it in mind. The trouble is that most organizations do not run a modern, cloud-native estate — they run a sprawling mix of old applications, legacy protocols and systems that cannot do modern verification. That legacy estate is where Zero Trust initiatives quietly stall, and pretending otherwise is why so many never finish.
Read insight →
Cloud Security
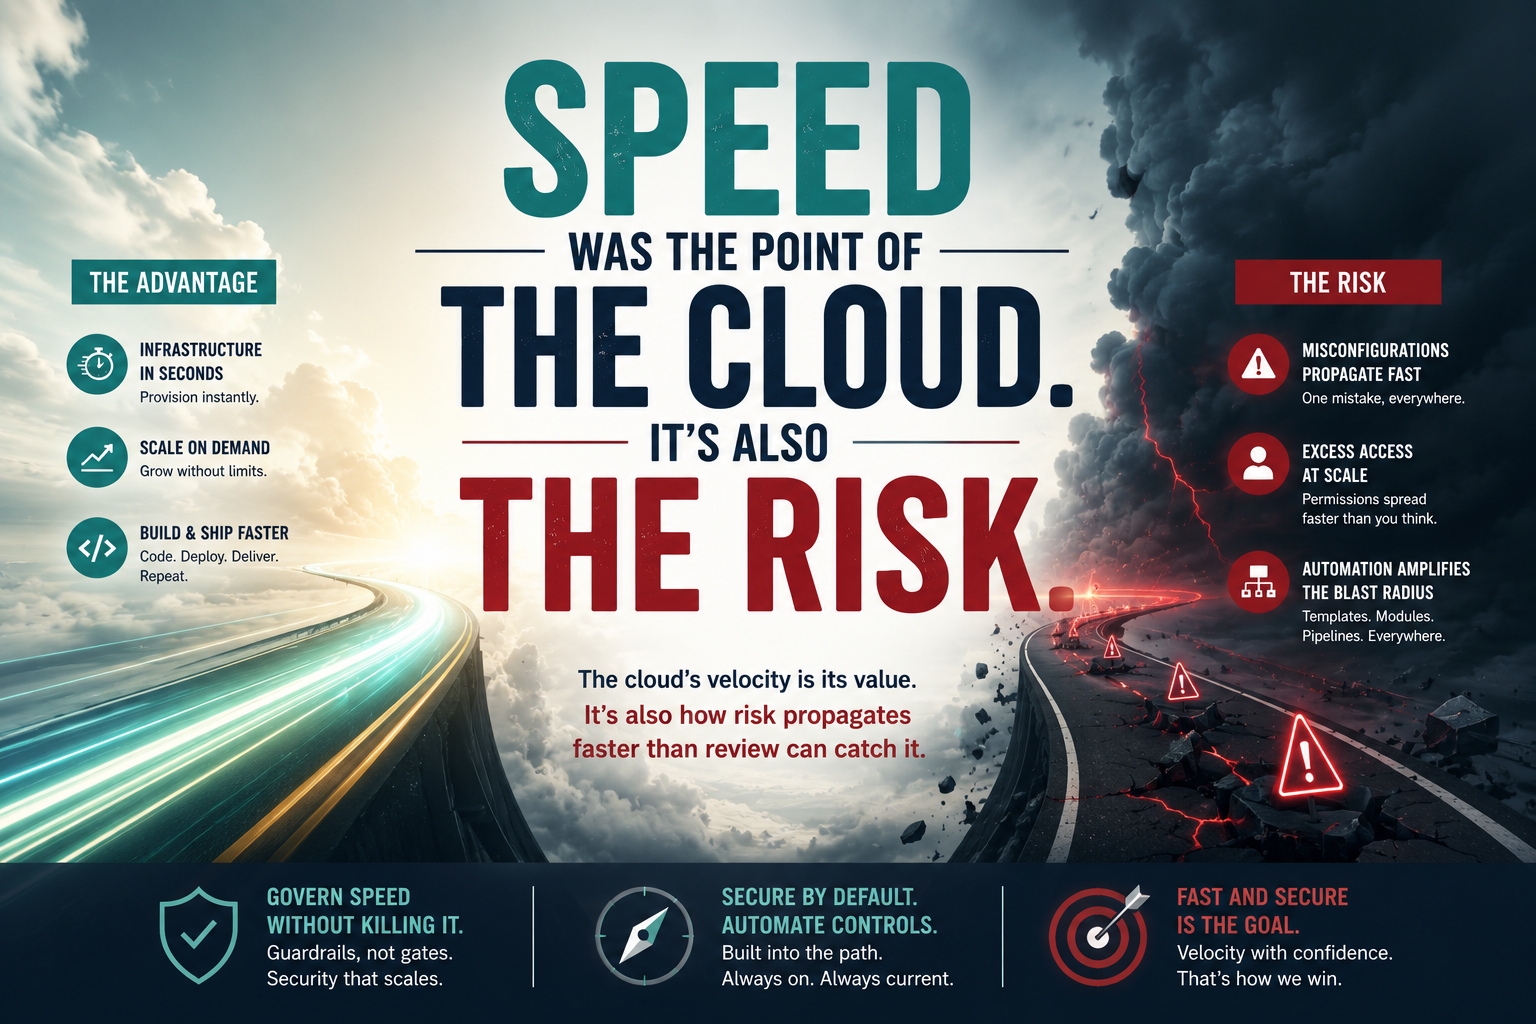
Speed Was the Point of the Cloud. It's Also the Risk.
The cloud's defining advantage is velocity — infrastructure created and changed in seconds, by anyone, through code. That same velocity is how misconfigurations and excess access propagate across an environment faster than any review can catch them. Securing the cloud means governing speed without killing it.
Read insight →
Endpoint Security
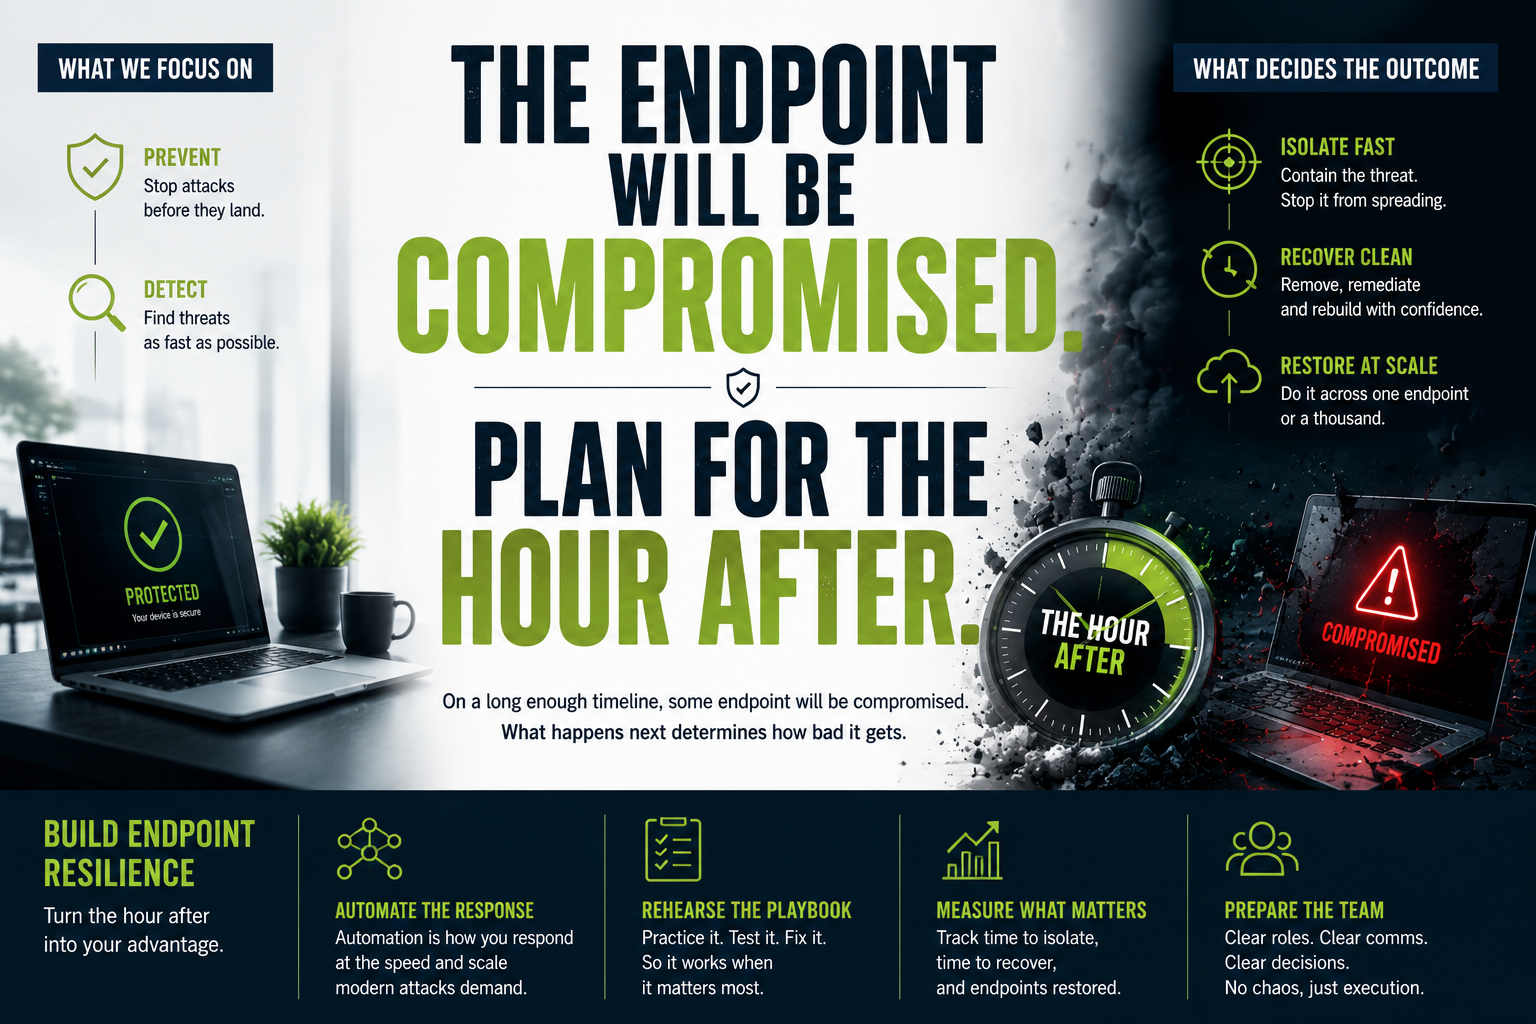
The Endpoint Will Be Compromised. Plan for the Hour After.
Endpoint security has been overwhelmingly about prevention and detection — stopping compromise and spotting it fast. But on a long enough timeline, some endpoint will be compromised, and what determines the damage is increasingly the speed and discipline of what happens next. Endpoint resilience — the ability to isolate, recover and restore at scale — is the underinvested half of the discipline.
Read insight →
Identity Security
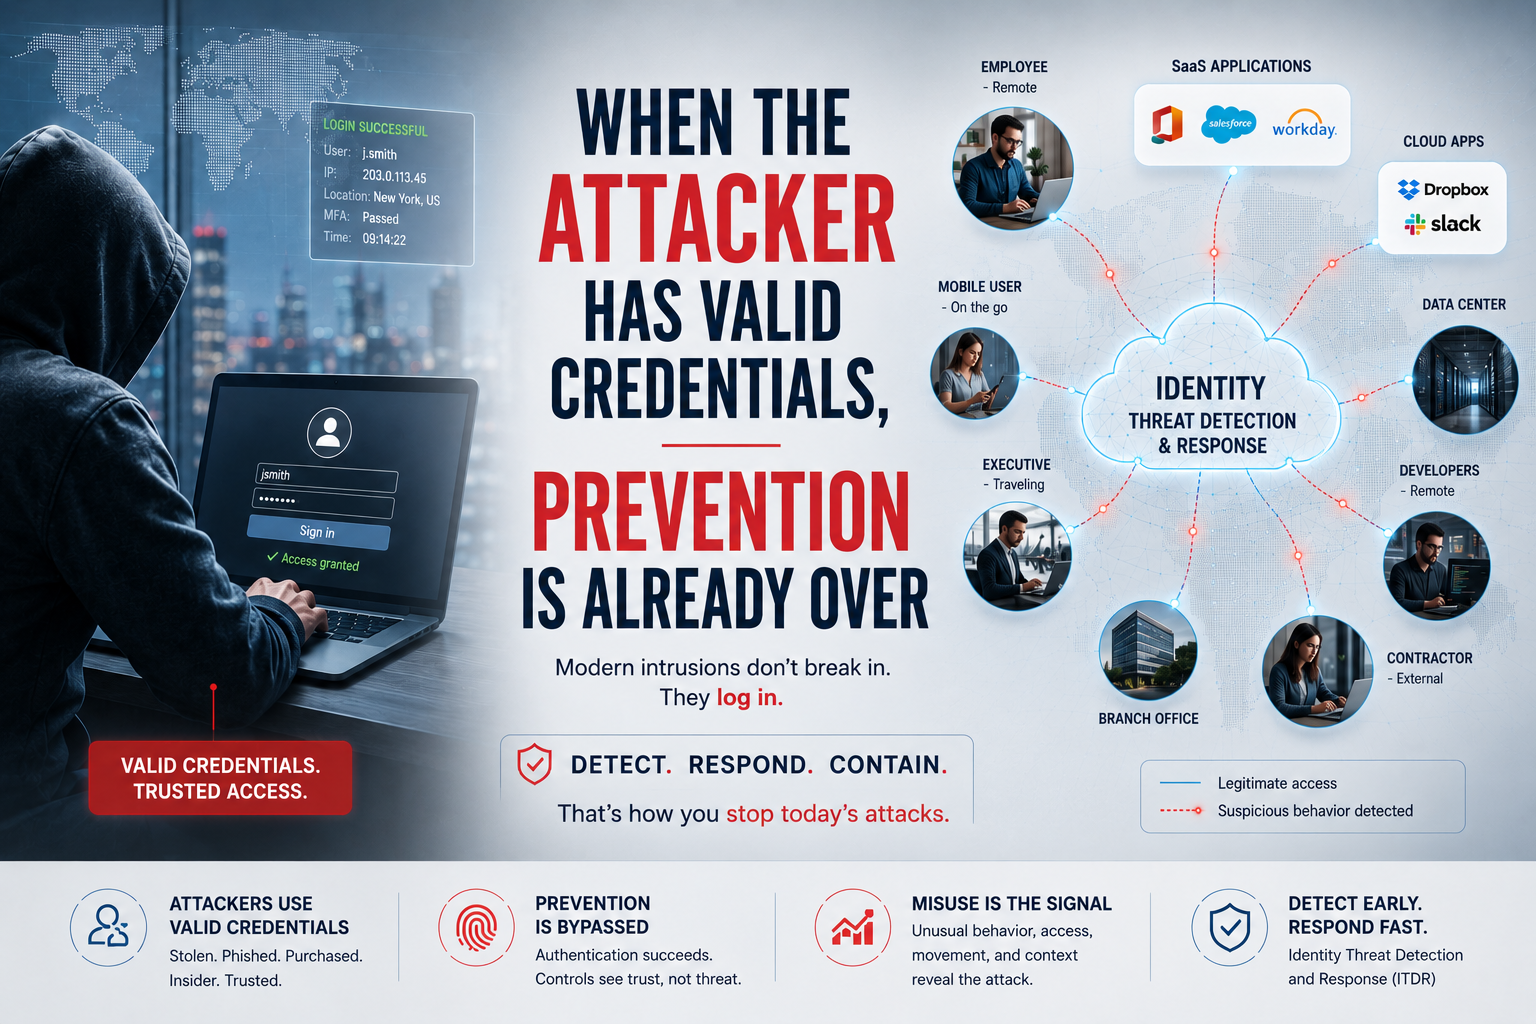
When the Attacker Has Valid Credentials, Prevention Is Already Over
The modern intrusion increasingly does not break in — it logs in. When an attacker operates through legitimate credentials, the controls designed to keep them out have already been bypassed. Identity threat detection and response exists because preventing access is no longer enough; the organization has to detect the misuse of access it has granted.
Read insight →
Threat Intel
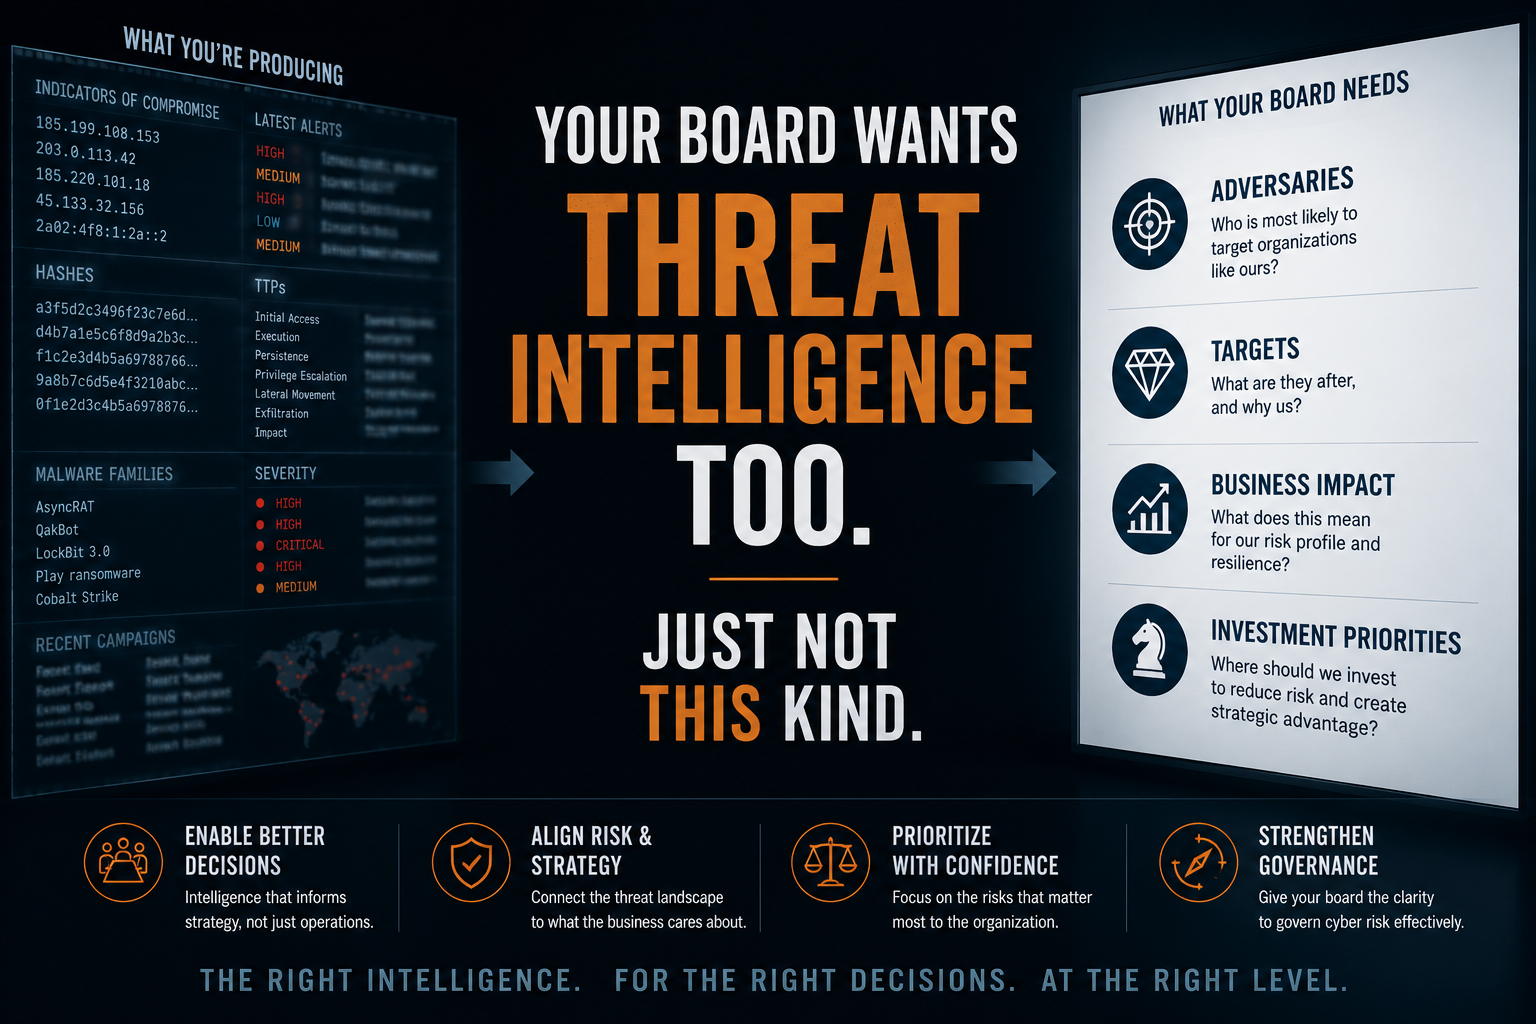
Your Board Wants Threat Intelligence Too — Just Not the Kind You're Producing
Most threat intelligence is tactical and operational — indicators, campaigns, adversary techniques aimed at the SOC. But executives and boards have intelligence needs too, and they are almost never met. Strategic threat intelligence translates the threat landscape into the decisions leaders actually make, and producing it is a distinct discipline most programs never build.
Read insight →
Data Security
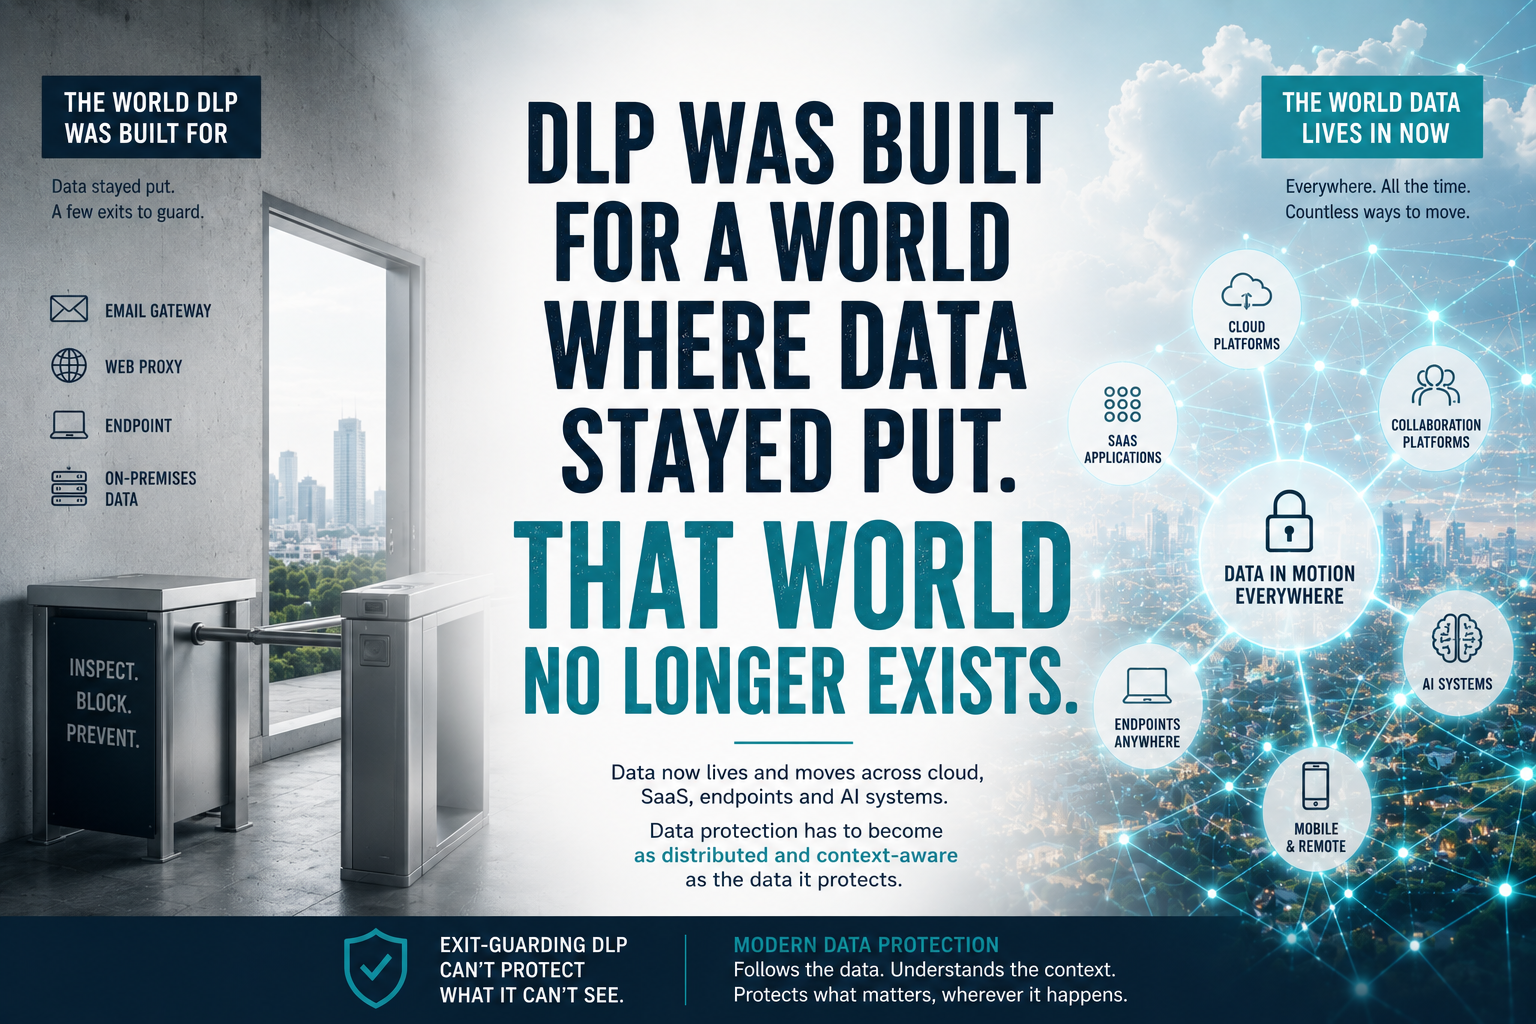
DLP Was Built for a World Where Data Stayed Put
Traditional data loss prevention was designed to guard a small number of exits from a contained environment. That environment no longer exists. Data now lives and moves across cloud, SaaS, endpoints and AI systems, and the pattern-matching, exit-guarding model of classic DLP struggles to follow it. Data protection has to become as distributed and context-aware as the data it protects.
Read insight →
Cyber Risk
Geopolitical Risk Has Become a Cybersecurity Problem
The line between geopolitical events and enterprise cyber risk has effectively disappeared. CISOs who do not have a framework for monitoring and responding to geopolitical developments are operating with a significant blind spot.
Read insight →
Board Strategy
If You Cannot Measure It, You Cannot Govern It
Most security metrics measure activity, not outcomes. The gap between what security teams report and what boards actually need to govern cyber risk effectively is one of the most consequential blind spots in enterprise security.
Read insight →
Cyber Risk
M&A Due Diligence Has a Cyber Problem
Mergers and acquisitions routinely transfer security debt, active compromises, and architectural liabilities that standard financial due diligence never surfaces. The cyber dimension of M&A is still dramatically underinvested.
Read insight →
Cyber Risk
Security Debt Is the Risk Nobody Wants to Talk About
Organizations have spent years accumulating security debt — deferred investments, legacy systems, unaddressed vulnerabilities, and architectural decisions that made sense at the time. That debt is now coming due.
Read insight →
SASE
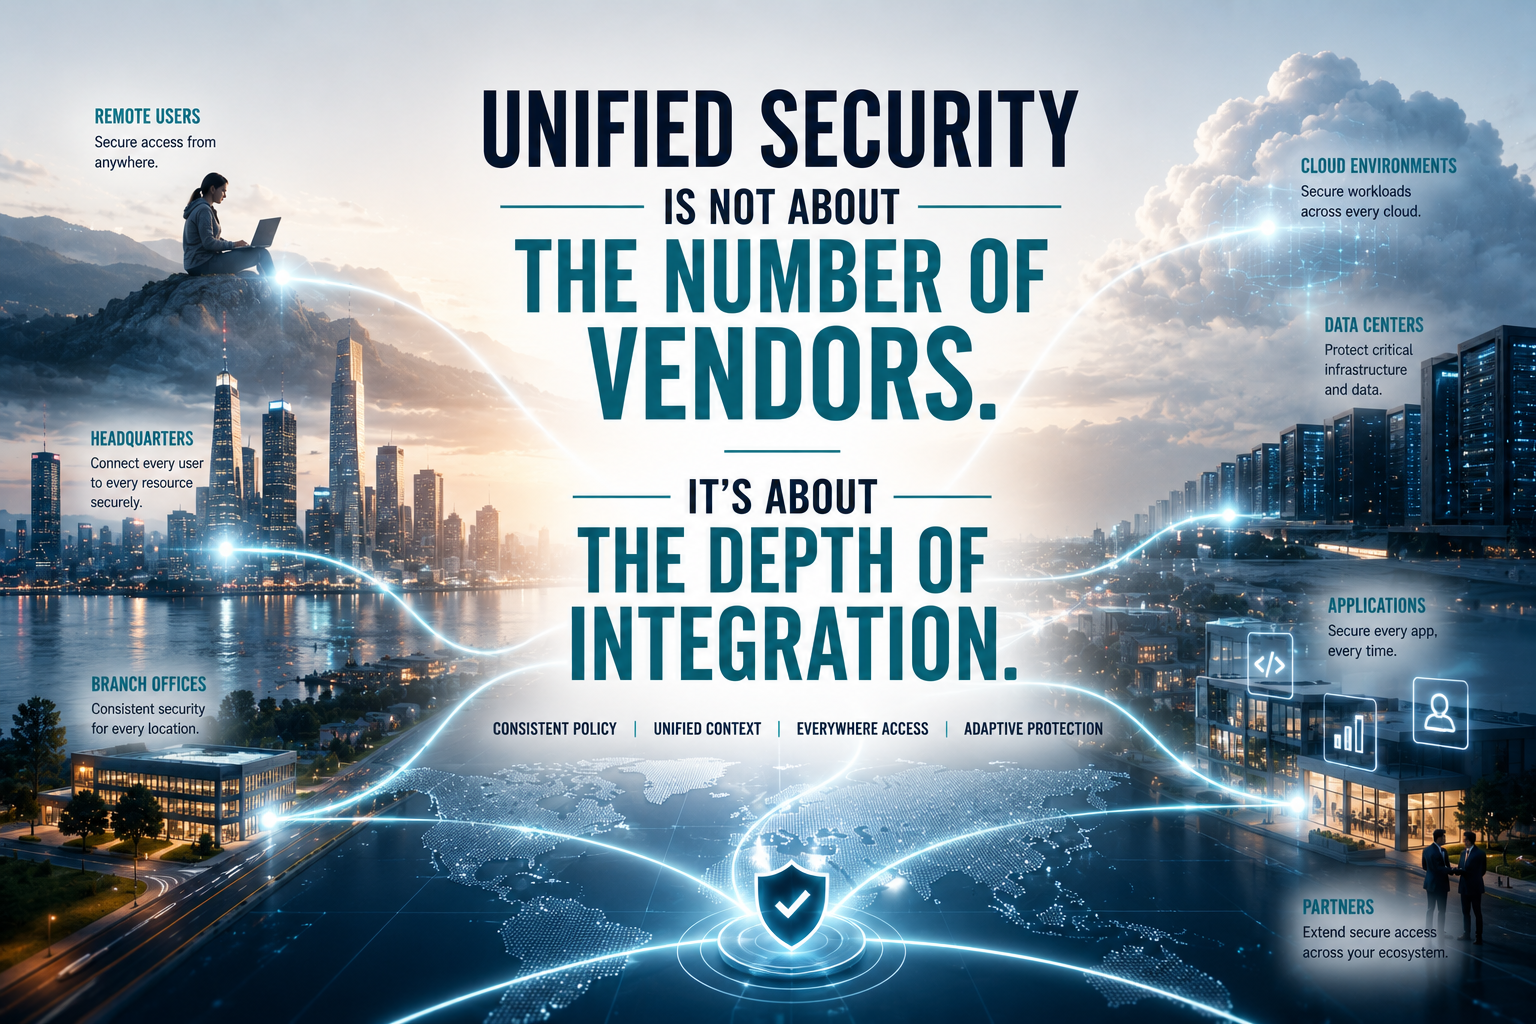
Single-Vendor SASE or Best-of-Breed? You're Asking the Wrong Question.
The dominant debate in SASE adoption is whether to consolidate on one vendor or assemble best-of-breed components. It is a debate that frames the decision around vendor ideology when the thing that actually determines success is something else entirely: the depth of integration and the consistency of policy. Here is how to make the decision on the terms that matter.
Read insight →
API Security
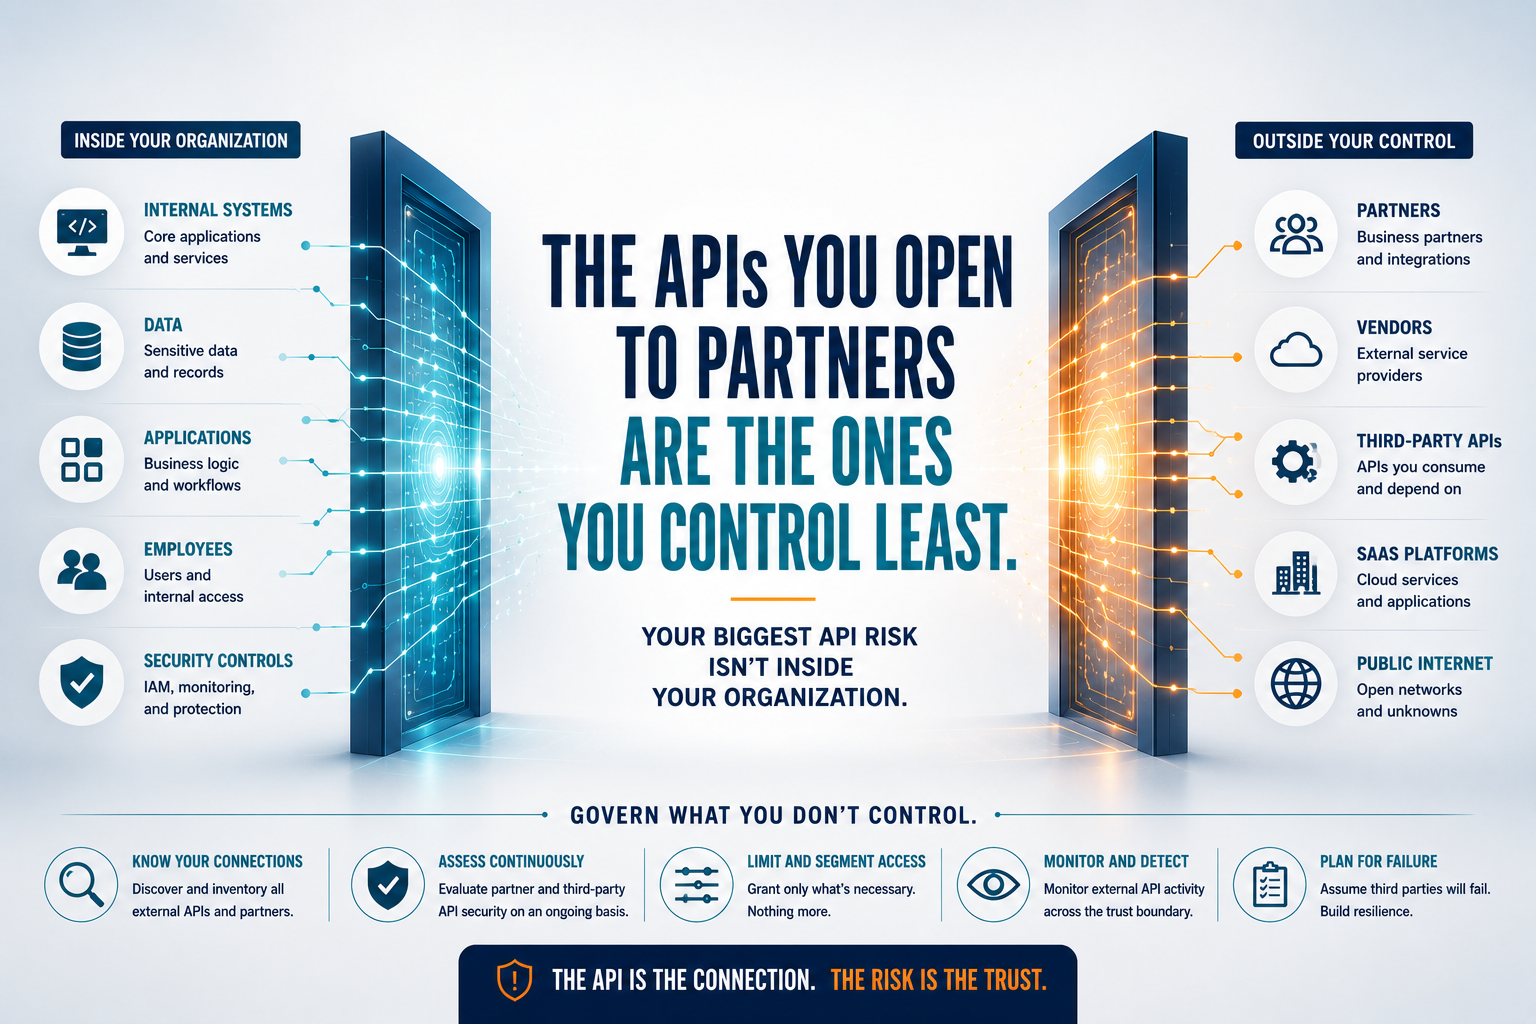
The APIs You Open to Partners Are the Ones You Control Least
Internal API security is hard enough. But the APIs an organization exposes to partners, and the third-party APIs it consumes, introduce a trust boundary that runs straight through the business. These external API relationships carry risk that internal controls do not reach — and most organizations govern them far more loosely than the dependence warrants.
Read insight →
Board Strategy
The CISO Is No Longer a Technical Role
The most effective CISOs in 2026 are operating as business executives who happen to understand technology — not technologists who learned to present to boards.
Read insight →
Cloud Security
The Cloud Shared Responsibility Model Has a Gap — And It Is Yours
Cloud providers are responsible for the security of the cloud. You are responsible for security in the cloud. That distinction has caused more enterprise breaches than any sophisticated attack technique.
Read insight →
Security Operations
The Human Factor Is Not a Training Problem
Organizations spend billions on security awareness training every year and continue to be breached through the same human vectors. The problem is not that employees need more training — it is that training alone is the wrong solution.
Read insight →
Zero Trust
The Next Insider Threat May Not Be Human
AI agents are rapidly acquiring the access, persistence and operational authority of privileged insiders — without the governance controls organizations spent decades building.
Read insight →
Cyber Risk
What Cyber Insurance Actually Covers — And What It Does Not
Cyber insurance has become a standard line item in enterprise risk management — but most organizations significantly overestimate what their policy actually covers when an incident happens.
Read insight →
Cloud Security
You Cannot Protect Data You Cannot See
Data proliferation has outpaced data governance in most enterprises. Organizations are protecting data they know about while leaving vast amounts of sensitive, unclassified, and ungoverned data exposed to both external attackers and internal misuse.
Read insight →
Cyber Risk
Your Third-Party Risk Program Is Probably a Fiction
Most enterprise third-party risk programs create the appearance of governance without the substance. The gap between what organizations think they know about vendor risk and what they actually know is widening.
Read insight →
AI Security
AI Security Is Becoming an Executive Function
AI security cannot be delegated to engineering or compliance. The risks are material, the decisions are consequential, and the cross-functional coordination required spans the entire C-suite. The organizations that are managing it well have made it an executive-level governance responsibility — not a department-level technical one.
Read insight →
API Security
API Security Is Becoming an Enterprise Risk Layer
APIs have quietly become the connective tissue of the modern enterprise — and one of its largest unmanaged risk surfaces. The organizations that are still treating API security as an application development concern are systematically underestimating a category of exposure that is growing faster than their visibility into it.
Read insight →
Cyber Risk
Cybersecurity Investment Prioritization in 2026
The era of automatic security budget growth is ending. The organizations that navigate this transition successfully are the ones that can connect every security investment to a measurable risk reduction outcome — not in theory, but in practice.
Read insight →
Board Strategy
Executive Lessons from Recent Ransomware Cases
The most important lessons from ransomware incidents are not technical. They are organizational — about decision-making under pressure, resilience assumptions that turned out to be wrong, and the gap between documented plans and operational reality.
Read insight →
Security Operations
How CISOs Should Restructure Security Operations
The security operations model that served enterprises for the past two decades is structurally inadequate for the threat environment of 2026. Restructuring is not a technology problem — it is an organizational and design problem that requires explicit executive choices.
Read insight →
Zero Trust
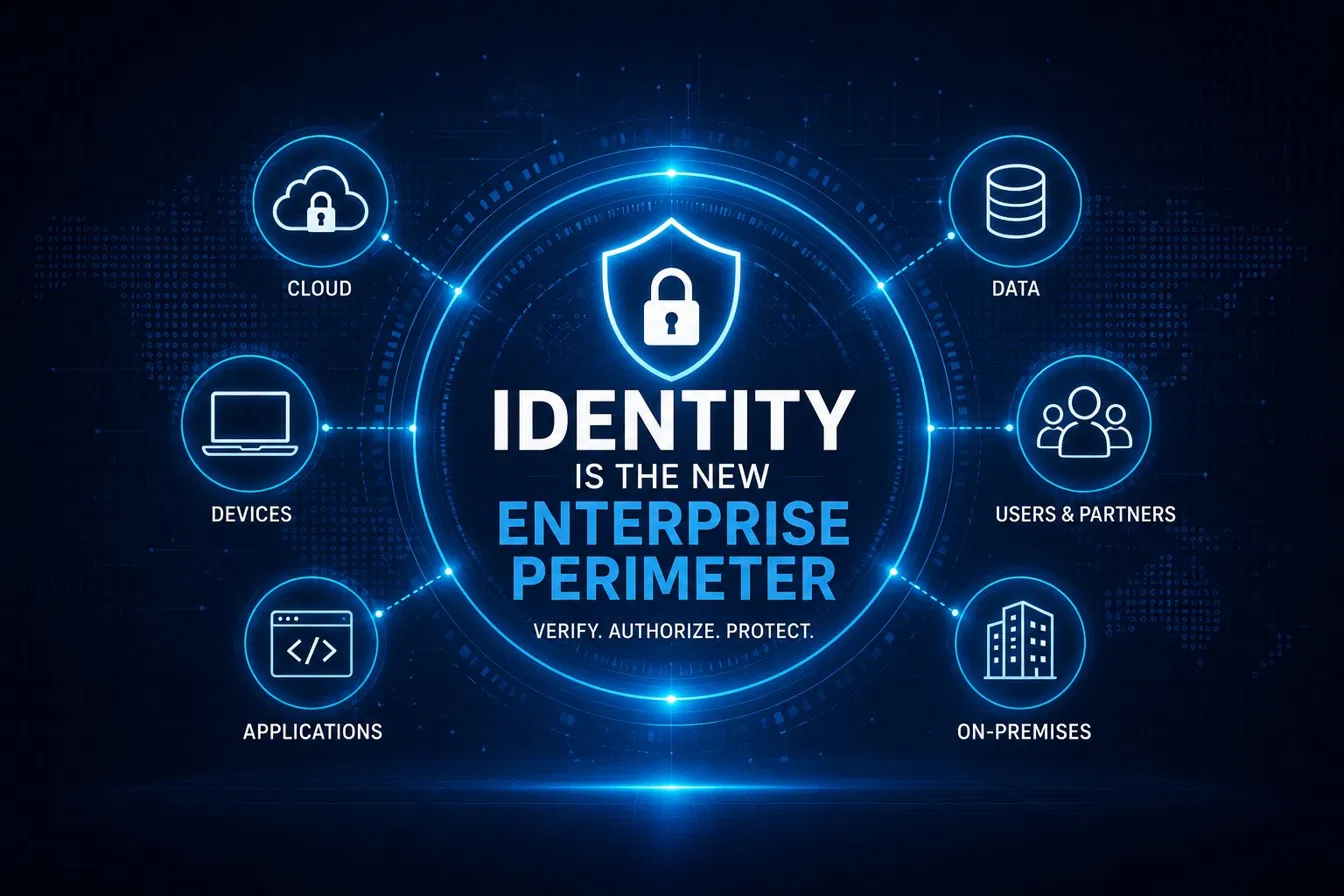
Identity Is the New Enterprise Perimeter
The network perimeter that defined enterprise security for three decades has dissolved. Identity — who or what is allowed to act, and under what conditions — has taken its place as the fundamental control boundary of the modern enterprise.
Read insight →
OT Security
OT Security Is Becoming a Board-Level Issue
Operational technology risk has crossed the threshold from an engineering concern to a board-level business risk. The organizations that have not made that transition in their governance model are carrying exposure that their boards do not fully understand.
Read insight →

Cyber Risk
The Collapse of Traditional Vulnerability Management
Counting CVEs and chasing patch SLAs has become one of the most expensive and least effective ways to manage security risk. The organizations that are getting vulnerability management right in 2026 are doing something fundamentally different — and the difference shows in actual breach outcomes.
Read insight →
Security Operations
The Death of the Traditional SOC?
AI will not eliminate 24x7 cyber visibility — but it will make the traditional alert-processing SOC economically and operationally indefensible. The organizations that understand this early will build something much more powerful in its place.
Read insight →

AI Security
The Executive AI Security Framework for 2026
AI security needs an executive framework — not another policy document, but a governance architecture that connects ownership, controls, evidence, and board accountability into a system that actually manages risk where it lives.
Read insight →
Board Strategy
The Future Cyber Workforce Problem Nobody Is Solving
The cybersecurity industry is focused on how AI will reduce the demand for repetitive security work. Almost nobody is focused on the downstream consequence — that removing the repetitive work also removes the learning environment through which most security expertise has historically been developed.
Read insight →
Board Strategy
The New Cyber Risk Conversation with Boards
Boards are no longer accepting technical dashboards as cyber governance. They are asking harder questions about resilience, exposure, and business impact — and most CISOs are not yet answering them well.
Read insight →
AI Security
The Rise of Agentic Attack Surfaces
AI agents do not just generate content — they act. They call tools, access data, invoke APIs, and trigger workflows with delegated enterprise authority. That operational capability has created an attack surface that most security programs are not yet designed to govern.
Read insight →
AI Security
The Rise of AI-Augmented Cyber Operations
The future of cyber operations is not AI replacing analysts — it is AI compressing the time between detection and understanding, while human judgment remains the irreplaceable component for high-stakes decisions. The organizations that get this balance right will have a significant operational advantage.
Read insight →
Board Strategy
What CISOs Are Actually Prioritizing This Year
The CISO agenda in 2026 is not getting broader — it is getting more concentrated. The strongest security leaders are narrowing their focus deliberately, choosing depth over coverage, and building the accountability structures that make priorities stick across the enterprise.
Read insight →
Security Operations
What Happens to Tier-1 Analysts in the AI Era?
AI is not simply eliminating Tier-1 analyst work — it is transforming the entry point into the security profession at the same moment the profession is evolving most rapidly. The consequences for individual careers and organizational talent pipelines are more complex than the simple "AI replaces junior analysts" narrative suggests.
Read insight →
AI Security
Why AI Governance Is Becoming a Security Function
AI governance started as a compliance and ethics conversation. It has become a security function because the risks it addresses — data exposure, model manipulation, unauthorized access, and ungoverned autonomous action — are security risks operating at enterprise scale.
Read insight →

AI Security
Will MSSPs Survive the AI Shift?
AI will not eliminate managed security providers, but it will radically change
Read insight →
AI Security
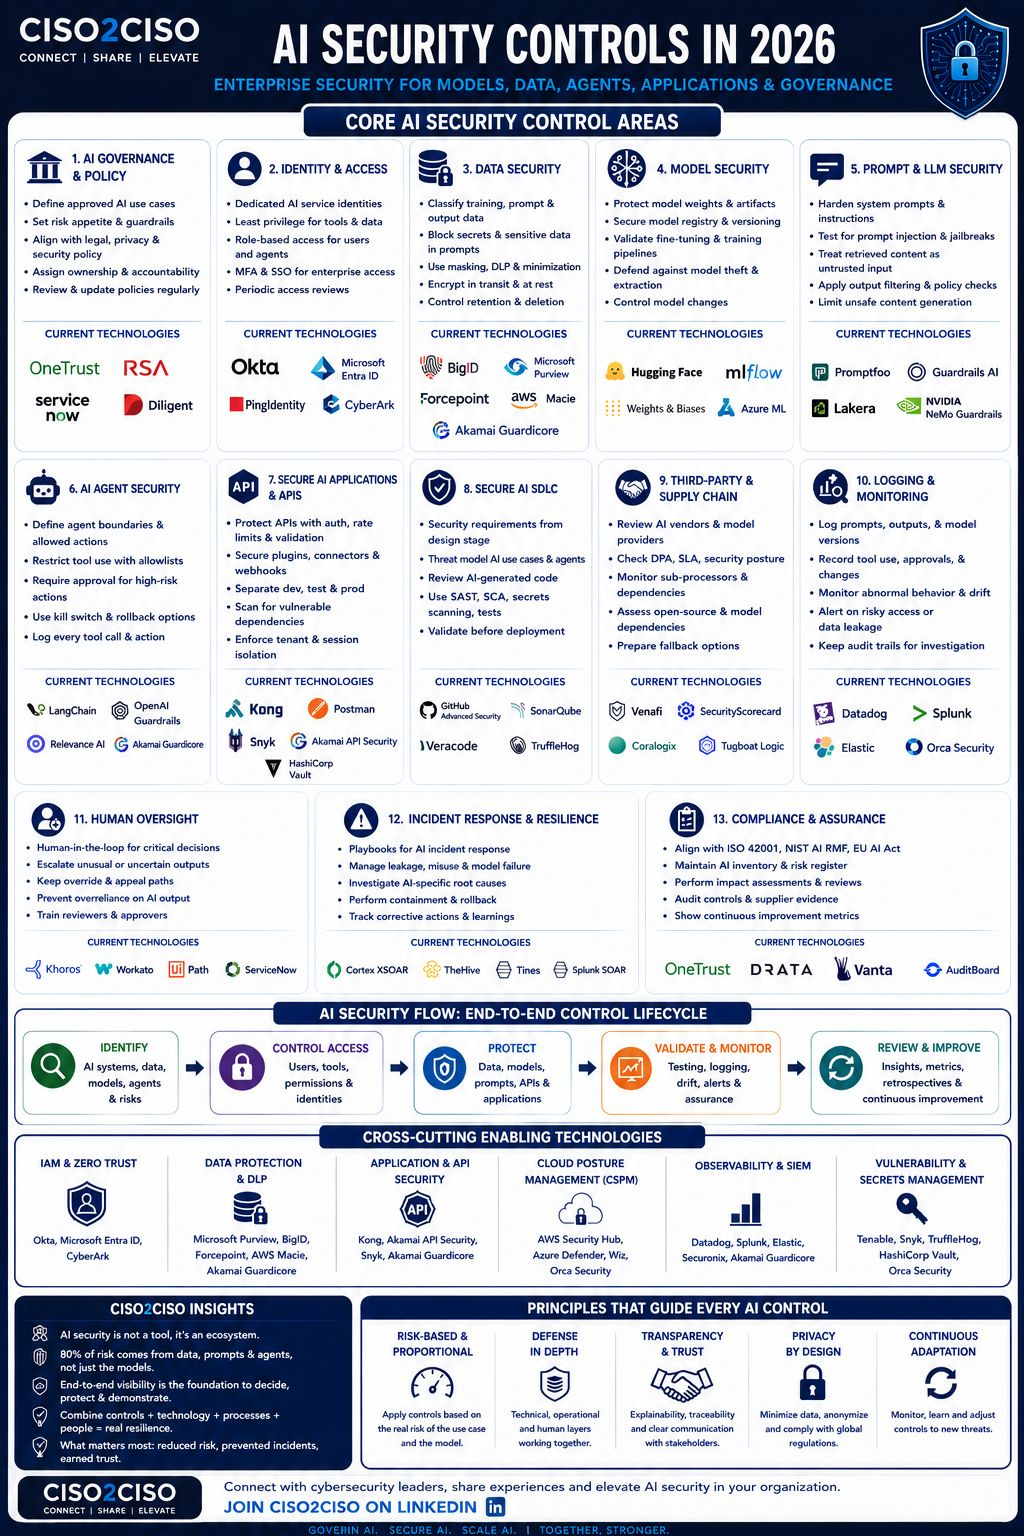
AI Security Is Moving from Frameworks to Operating Models
CISOs are shifting AI security from theoretical controls into implementable ecosystems across models, data, agents, applications and governance. The question is no longer whether controls exist — it is whether they are operational, owned and evidenced.
Read insight →
OT Security
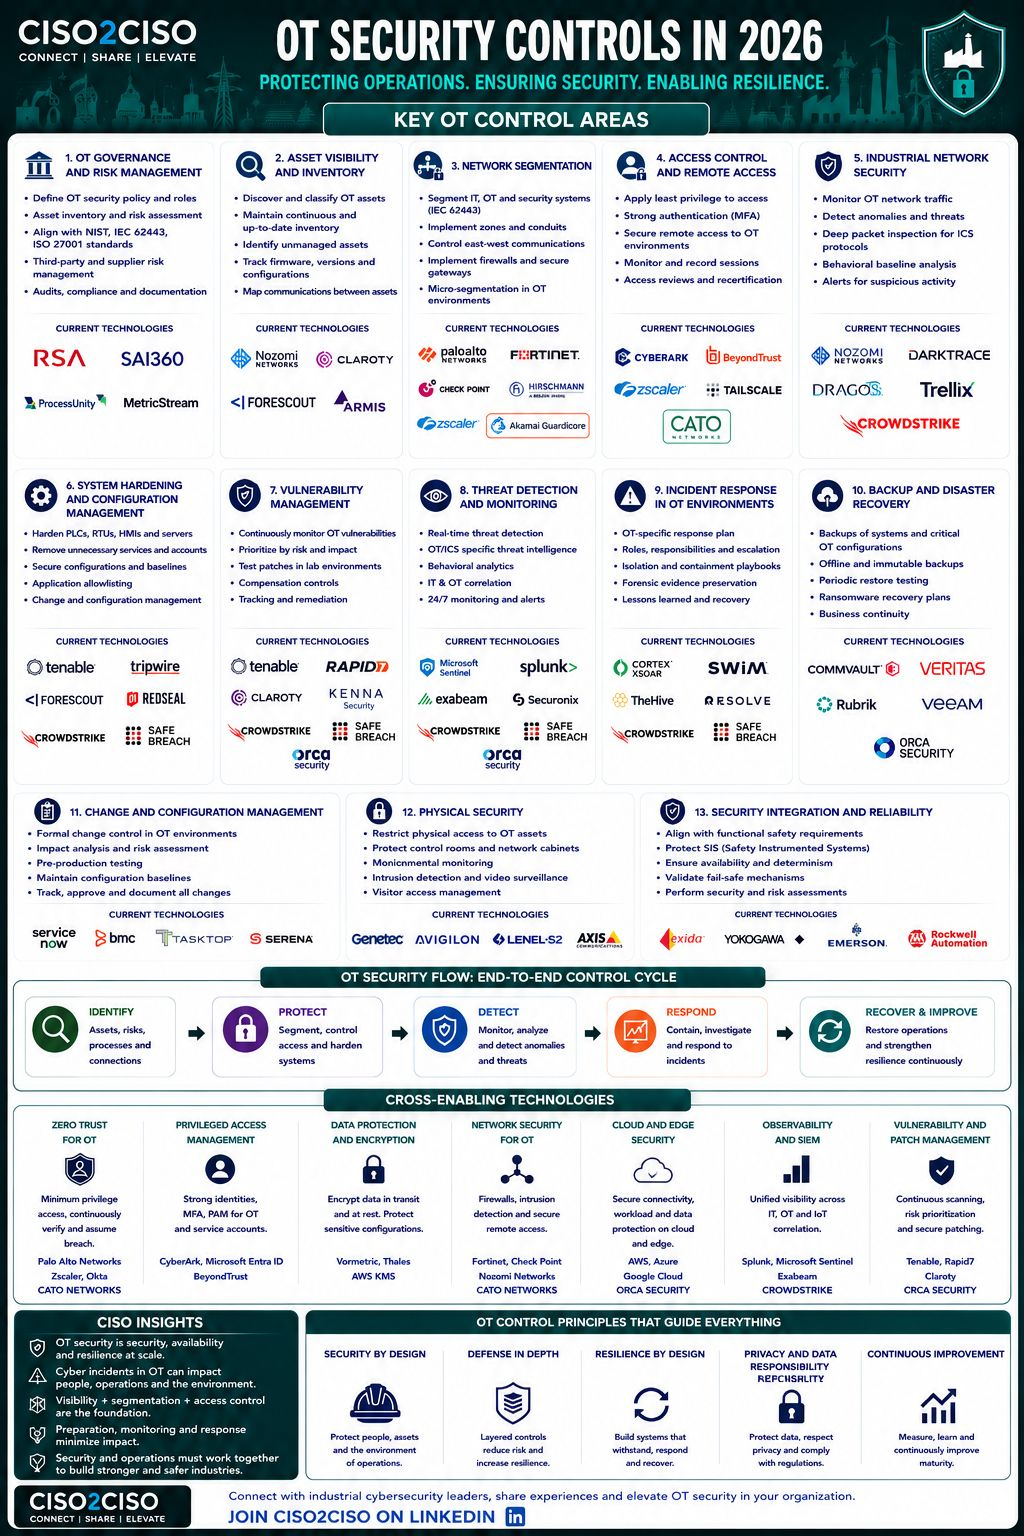
OT Security Is Becoming an Enterprise Resilience Challenge
IT/OT convergence is transforming industrial security from a plant-level protection problem into a strategic business continuity issue. OT incidents now carry consequences that reach far beyond the plant floor — into production, safety, supply chain and regulatory liability.
Read insight →
AI Security
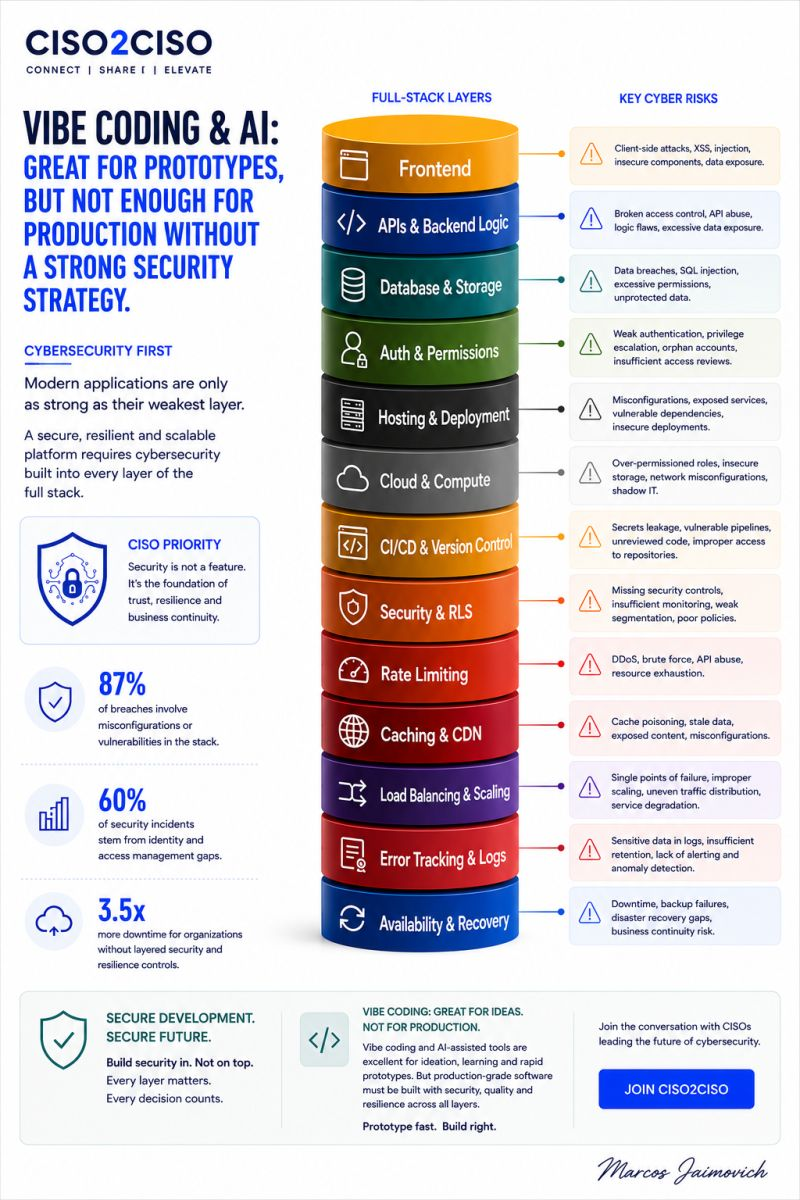
Vibe Coding Accelerates Prototypes — But Production Requires Security Architecture
AI-assisted development is accelerating delivery across enterprise teams. The risk is not the technology — it is the false production maturity that occurs when prototypes move into enterprise environments without the security architecture that production requires.
Read insight →
Threat Intel
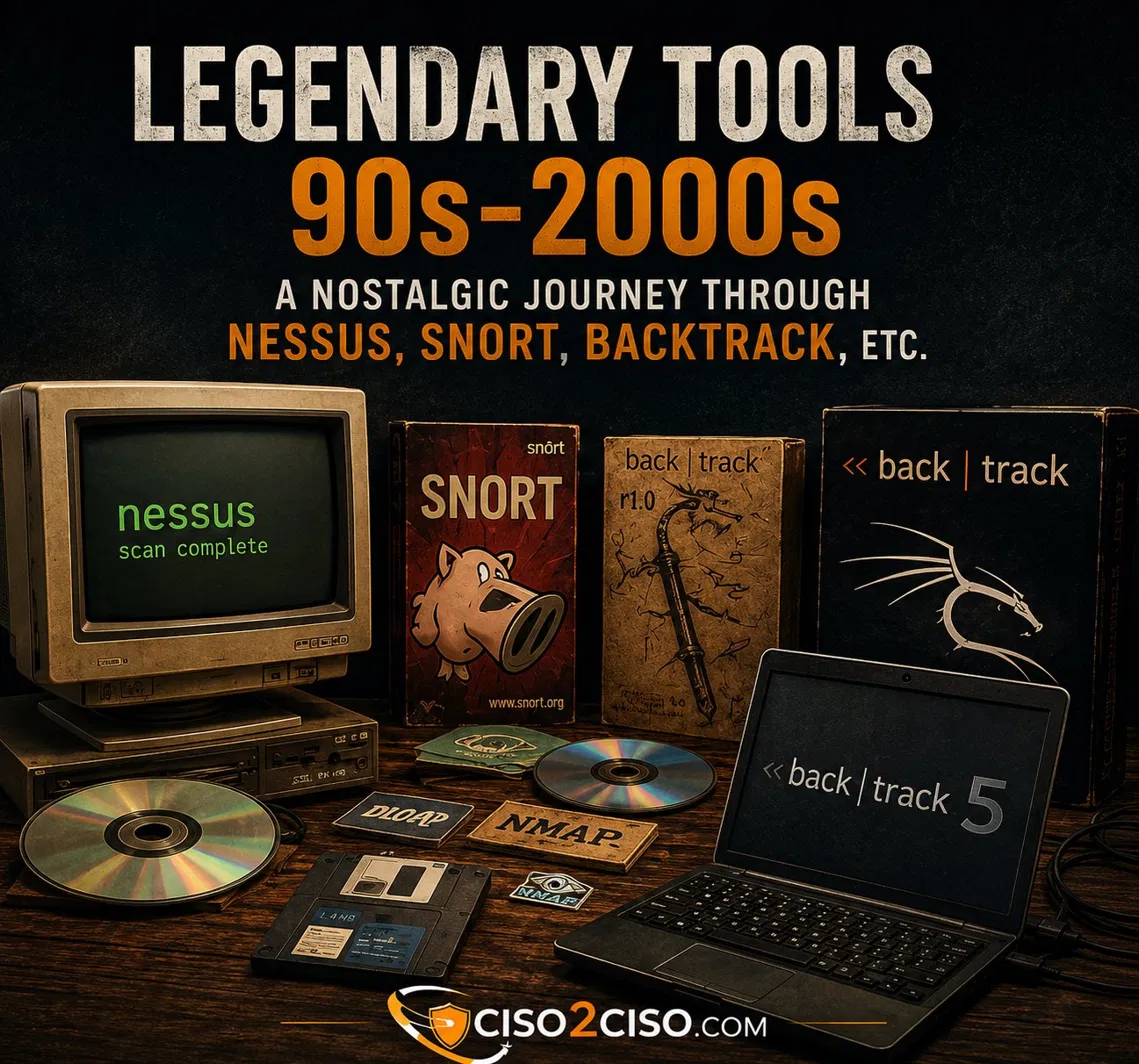
Do You Remember These Security Tools? A Nostalgic Journey Through the Tools That Forged Cybersecurity (90s–2000s)
Before EDR, XDR and cloud-native platforms, there was Nessus in open source form, Snort writing custom rules at 2am, BackTrack as our portable university, and L0phtCrack teaching us everything we needed to know about password hygiene. A tribute to the tools that educated a generation of security professionals.
Read insight →
Cyber Risk
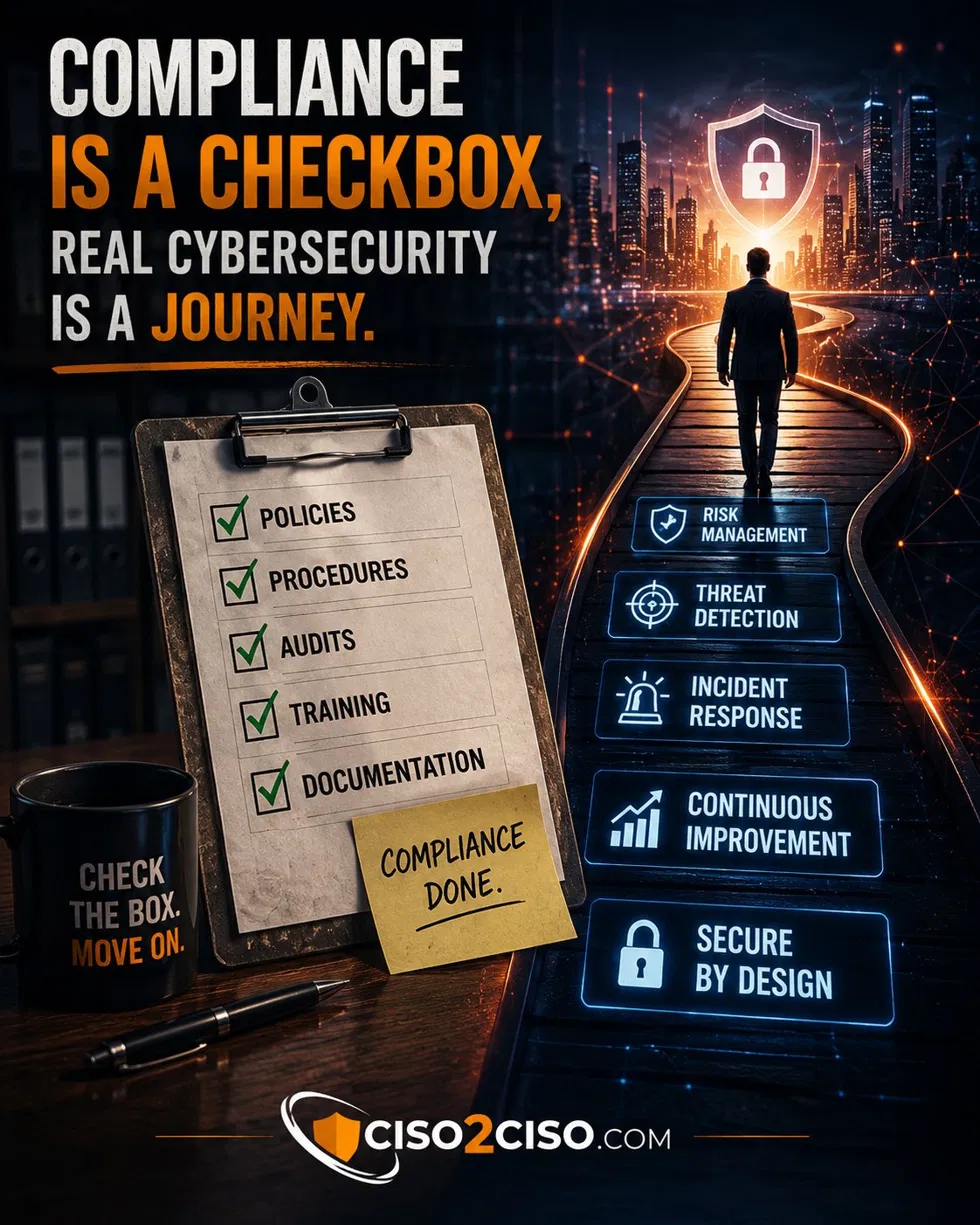
Compliance Is a Checkbox. Real Cybersecurity Is a Journey.
Achieving compliance does not equate to comprehensive security. This is not a technicality — it is one of the most dangerous misconceptions in enterprise cybersecurity. Compliance is foundational but not all-encompassing. Real security requires operational controls, automation and continuous improvement — not just passing audits.
Read insight →
Threat Intel
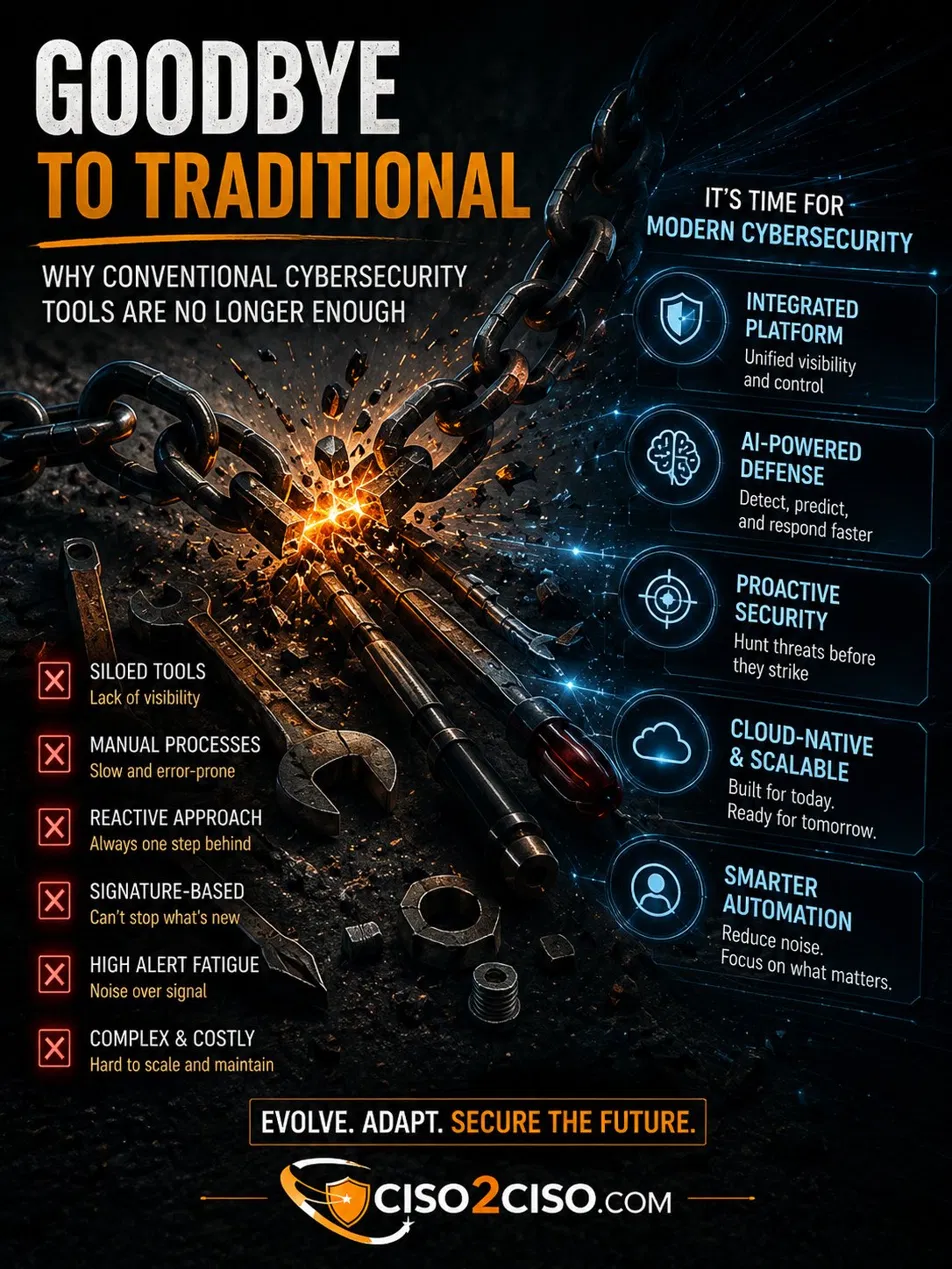
Goodbye to Traditional: Why Conventional Cybersecurity Tools Are No Longer Sufficient
As the digital threat landscape evolves in complexity, traditional cybersecurity tools — firewalls, signature-based antivirus, static SIEM rules — increasingly fail to provide adequate protection. The question is not whether to modernize. It is how to build the security architecture the current threat environment actually requires.
Read insight →
Leadership & Strategy
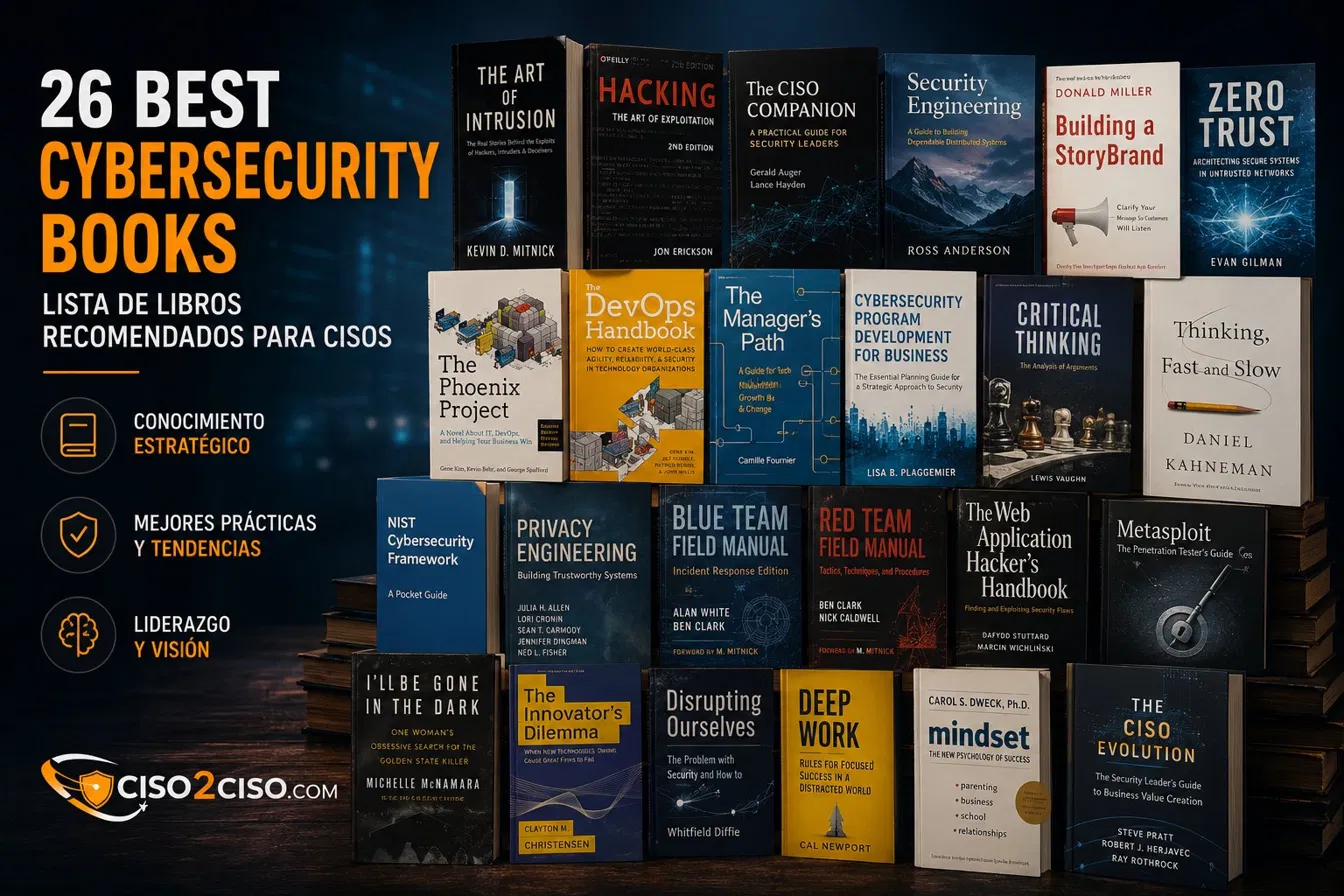
The 26 Best Cybersecurity Books Every CISO Should Read
A curated personal reading list of 26 essential cybersecurity books for CISOs and security professionals — covering ransomware defense, SOC design, security metrics, leadership, risk governance and the human dimensions of cybersecurity.
Read insight →
Board Strategy
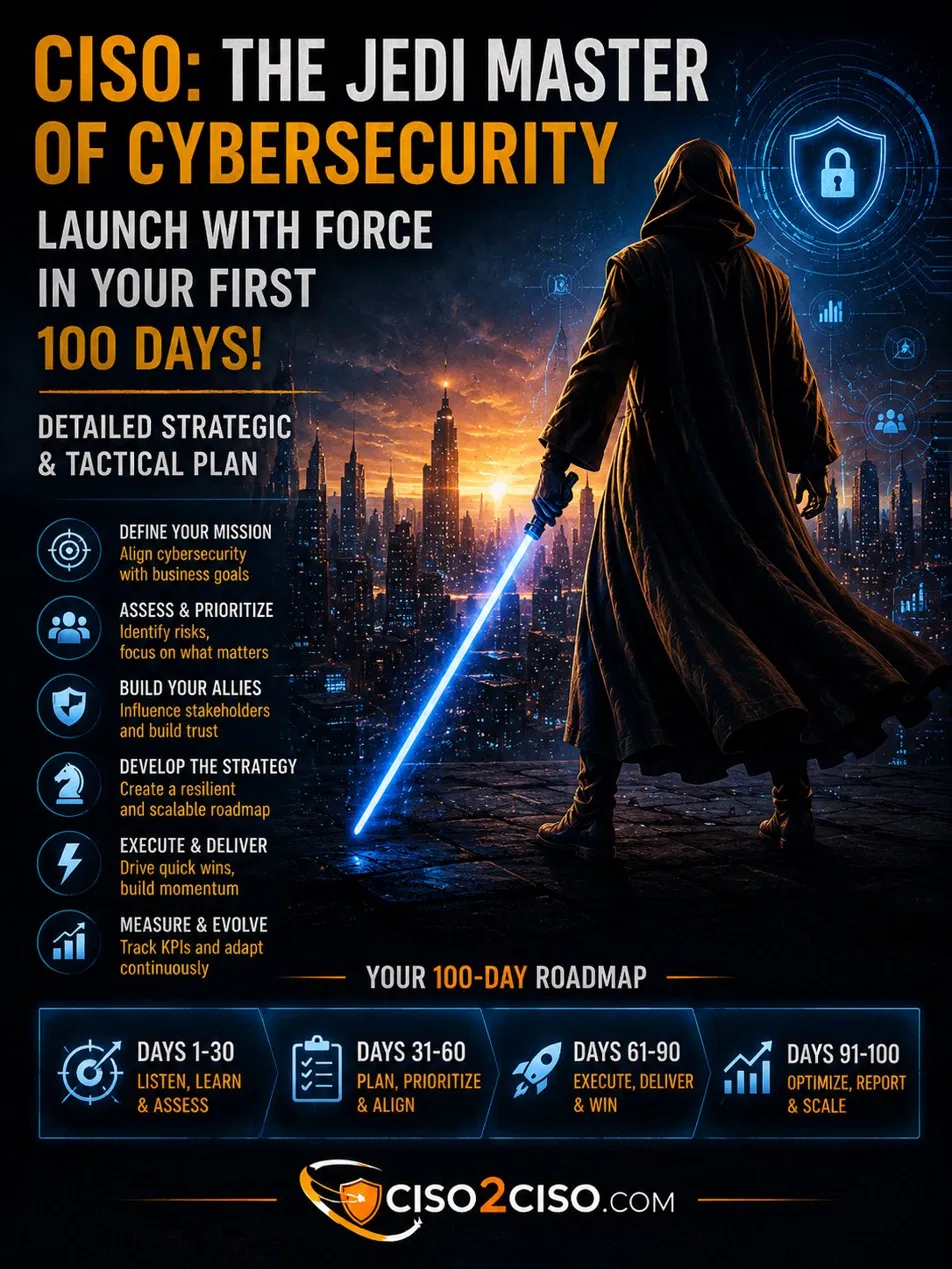
The CISO's First 100 Days: A Strategic and Tactical Playbook
The first 100 days as CISO represent a critical and unrepeatable window to establish the foundation of the security program. This strategic and tactical plan covers the four phases that take a new CISO from active listening to credible execution with visible results.
Read insight →